AI and Cyber Threat Detection in 2026: How It Can Reduce MTTD and Dwell Time
Artificial intelligence is increasingly becoming part of modern cybersecurity detection workflows.
Security teams use AI-assisted tools to help analyze:
- authentication activity;
- endpoint telemetry;
- cloud logs;
- network behavior;
- threat intelligence;
- user and entity behavior;
- large volumes of security alerts.
The goal is not simply to “use AI.”
The goal is to answer a more important question:
Can AI help security teams discover meaningful malicious activity sooner without creating unacceptable false positives, false negatives, or operational risk?
In 2026, that question matters because attackers are also using AI.
IBM’s 2026 Cost of a Data Breach research reports a 56% increase in AI-driven attacks, while the global average breach cost reached $4.99 million. IBM also reports that organizations using AI and automation extensively in security achieved an average $1.93 million reduction in breach costs compared with organizations using none.
AI can improve detection.
But it does not magically create visibility where no telemetry exists.
A useful formula is:
Strong telemetry + strong detections + AI-assisted analysis + human validation = better detection performance
not:
AI = instant security.
AI Cyber Threat Detection at a Glance
| Detection area | How AI can help | What still matters |
|---|---|---|
| Behavioral anomalies | Identify unusual activity patterns | Good baselines and context |
| Identity detection | Flag suspicious logins and privilege changes | Identity telemetry |
| Alert correlation | Connect related events | Accurate source data |
| Threat prioritization | Rank suspicious activity | Business context |
| Cloud monitoring | Detect unusual IAM/API behavior | Cloud audit logging |
| Threat hunting | Surface weak signals across large datasets | Analyst interpretation |
| Malware analysis | Classify suspicious behavior faster | Validation and sandboxing |
| SOC triage | Summarize and enrich alerts | Human review |
| Detection engineering | Help write and refine rules | Testing and tuning |
AI works best as a force multiplier for a mature detection program.
Table of Contents
What Does “AI Reducing Breach Detection Time” Mean?
The phrase should not imply that AI has one universal measurable effect.
AI may reduce detection time by improving specific parts of the detection workflow.
For example:
Without AI assistance
Alert generated
→ analyst manually checks user
→ analyst searches endpoint
→ analyst checks cloud logs
→ analyst searches threat intelligence
→ correlation completed
With AI-assisted workflow
Alert generated
→ automated enrichment
→ multi-source correlation
→ prioritized incident
→ analyst validation
If the second workflow reduces the time from malicious activity to meaningful detection, then AI has contributed to lower detection time.
That improvement should be measured using actual incident data.
MTTD: The Core Detection Metric
Mean Time to Detect (MTTD) measures the average detection interval across a defined group of incidents.
A simple formula is:
MTTD = Total Detection Time ÷ Number of Incidents
Example:
| Incident | Detection interval |
|---|---|
| A | 12 min |
| B | 30 min |
| C | 18 min |
| D | 60 min |
Total:
120 minutes
Incidents:
4
MTTD:
30 minutes
For the full metric methodology, see Mean Time to Detect (MTTD).
AI Does Not Automatically Lower MTTD
Imagine an organization has no logging for:
- VPN appliances;
- cloud identities;
- privileged SaaS activity;
- virtualization infrastructure.
An advanced AI system cannot reliably detect an attack from evidence that was never collected.
This is one of the most important points to make in your article.
Mandiant’s M-Trends 2026 specifically highlights attackers remaining undetected on edge devices that often lack standard telemetry, contributing to longer dwell time.
So before investing heavily in AI detection, organizations should ask:
Do we have the data AI needs to detect the threat?
Shift 1: Behavioral Anomaly Detection
Traditional security controls often depend on:
- signatures;
- known indicators;
- static rules.
Behavioral analytics can look for deviations from expected activity.
Examples:
- administrator logging in from unusual geography;
- service account accessing new systems;
- sudden privilege escalation;
- user downloading unusually large datasets;
- unfamiliar cloud API sequence;
- endpoint executing rare process chains.
AI and machine-learning models can help identify these patterns across large datasets.
The benefit is particularly useful for attacks that do not rely on known malware signatures.
Behavioral Detection Needs Good Baselines
A behavioral model can only be useful if normal behavior is reasonably understood.
Poor baselines can create:
- excessive false positives;
- missed attacks;
- alert fatigue.
For example:
“User logged in at midnight”
may be suspicious for one organization.
For a global 24/7 company, it may be completely normal.
Context matters.
Shift 2: Identity Anomaly Detection
Identity has become one of the most important detection surfaces.
Attackers frequently use:
- stolen passwords;
- session cookies;
- OAuth tokens;
- API keys;
- privileged accounts.
AI-assisted identity analytics can help identify combinations such as:
new device
unexpected location
privilege change
unusual data access
A single event may not be suspicious enough.
The combined pattern may be.
Identity Detection Example
Suppose:
10:00 — User signs in from known location.
10:03 — New OAuth consent granted.
10:05 — Account privilege increases.
10:08 — Large data export begins.
Traditional tools may generate four separate low-severity alerts.
AI correlation can help identify:
probable account takeover
and escalate the event sooner.
Shift 3: Cross-Source Alert Correlation
A major AI advantage is the ability to process events from multiple systems quickly.
Detection sources may include:
- SIEM;
- EDR;
- IAM;
- cloud logs;
- network telemetry;
- email security;
- SaaS platforms.
Google Cloud’s 2026 security operations guidance describes AI agents assisting with monitoring, detection, and response by bringing together security operations and AI threat-defense capabilities.
That supports a practical use case:
correlating weak signals into a stronger incident hypothesis.
Correlation Example
Consider these alerts:
Endpoint: PowerShell executes unusual command.
Identity: User logs in from new geography.
Cloud: User requests sensitive secrets.
Network: Device contacts suspicious infrastructure.
Individually:
Low-to-medium confidence.
Together:
Much higher confidence.
AI-assisted correlation can help shorten the time analysts spend connecting those events manually.
Shift 4: AI-Assisted Alert Triage
SOC teams often struggle with:
- high alert volume;
- duplicate alerts;
- low-priority noise.
AI can help triage by:
- summarizing alerts;
- adding context;
- ranking likely severity;
- identifying duplicates;
- suggesting likely attack techniques.
This can reduce analyst workload.
But speed is not enough.
Track:
- analyst override rate;
- false escalation rate;
- missed Critical incidents;
- time saved.
A fast triage system that prioritizes the wrong incidents is not an improvement.
Shift 5: AI-Assisted Threat Hunting
Threat hunting differs from normal alerting.
Instead of waiting for an alert, analysts proactively search for hidden adversary activity.
AI can help by:
- generating hypotheses;
- searching large log datasets;
- clustering suspicious activity;
- surfacing rare patterns;
- summarizing related events.
IBM’s 2026 reporting notes that organizations are increasingly using AI within threat hunting, response, and containment functions.
This can help identify attacks that did not trigger high-confidence alerts.
Threat Hunting Still Requires Analysts
AI may surface:
“These 17 authentication events appear unusual.”
A human still needs to determine:
- whether the activity is malicious;
- whether it has legitimate business context;
- what evidence supports escalation.
AI-assisted threat hunting should accelerate analysis.
It should not replace evidence-based investigation.
Shift 6: Cloud and SaaS Detection
Cloud environments produce huge volumes of telemetry.
Important events may involve:
- API calls;
- token issuance;
- IAM changes;
- storage access;
- role assumptions;
- service-account behavior;
- OAuth permissions.
AI can help identify suspicious sequences across these events.
Google’s current security guidance emphasizes continuous monitoring and AI-supported detection across modern cloud environments.
This can be particularly useful because cloud attacks may occur without any traditional malware.
Cloud Detection Example
09:00 — New API key created.
09:04 — Role elevated.
09:07 — Sensitive storage accessed.
09:12 — Logs disabled.
No malware.
No ransomware binary.
No endpoint alert.
The attack exists entirely in identity and cloud-control activity.
AI-assisted correlation can help connect the sequence.
Shift 7: AI-Assisted Detection Engineering
Detection engineers create rules that identify attacker behavior.
AI can assist with:
- drafting SIEM queries;
- converting detection logic;
- mapping techniques;
- identifying missing telemetry;
- generating test cases.
But generated detection rules must be tested.
AI may produce:
- inefficient queries;
- overly broad logic;
- false positives;
- unsupported assumptions.
Human validation remains essential.
Shift 8: Faster Security Investigation
AI can summarize large event sets.
Example:
An analyst receives:
2,000 authentication events
instead of reading them manually, AI can summarize:
- unusual locations;
- new devices;
- privilege changes;
- suspicious sequence;
- high-risk timestamps.
This can reduce investigation latency.
But:
AI summary ≠ raw evidence
The underlying logs should remain accessible.
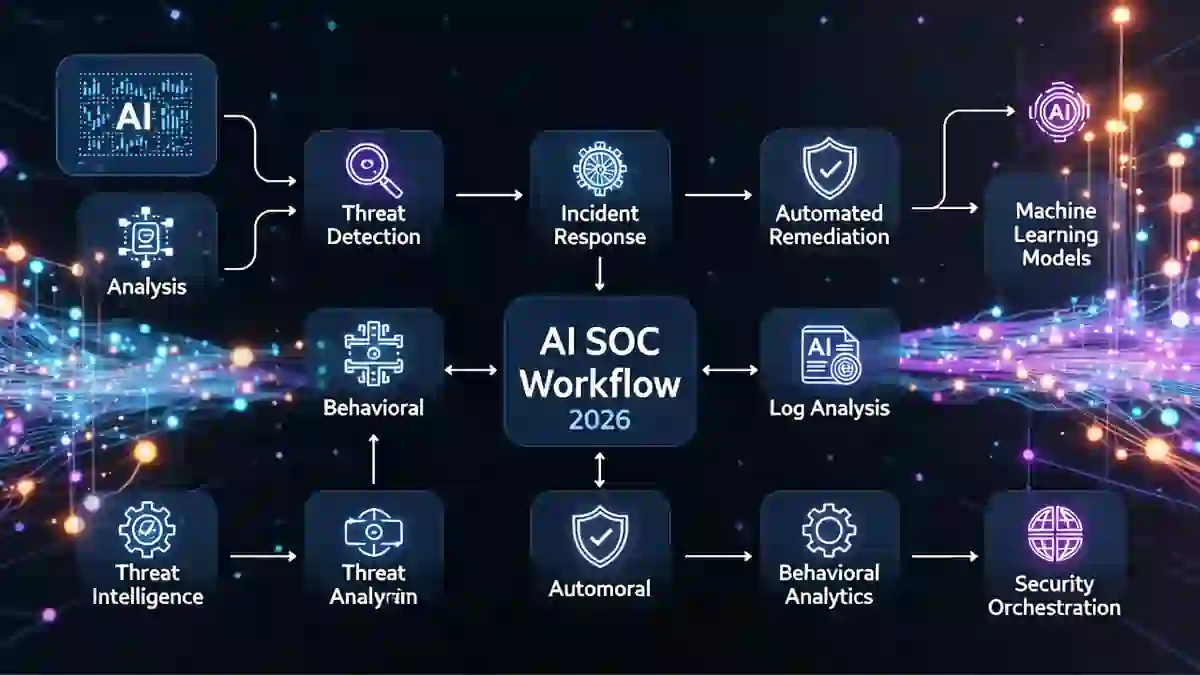
Shift 9: Faster Detection-to-Decision Workflow
Detection speed is not only about machine alerts.
The real timeline can be:
malicious activity
↓
alert
↓
analyst acknowledgement
↓
investigation
↓
incident validation
↓
response
AI may improve multiple stages:
- enrichment;
- prioritization;
- correlation;
- summarization.
This can reduce total time before meaningful defensive action begins.
For the wider response workflow, see AI and Incident Response Automation.
AI and Dwell Time
Dwell time generally measures the period between initial compromise and discovery.
Mandiant’s M-Trends 2026 reports a global median dwell time of 14 days across its 2025 investigations, compared with 11 days previously.
That does not mean:
global MTTD = 14 days
The statistic is median dwell time from Mandiant’s investigation dataset.
For the distinction, see:
and:
Can AI Reduce Dwell Time?
Potentially, yes.
AI may help discover hidden activity sooner by improving:
- identity anomaly detection;
- threat hunting;
- telemetry correlation;
- behavioral detection;
- cloud monitoring.
But there is no guarantee.
If the compromised environment lacks telemetry, dwell time can remain high regardless of AI capability.
AI Cannot See What Is Not Logged
This should be one of the strongest sentences in the article:
AI cannot reliably detect activity for which the organization has no usable telemetry.
Before deploying advanced AI, verify visibility across:
- endpoints;
- identity;
- cloud;
- VPN;
- network;
- SaaS;
- virtualization;
- critical edge devices.
Mandiant’s 2026 findings about long-term persistence on edge devices reinforce this point.
Mean vs Median Detection Time
AI-performance measurement should not use only the mean.
Example detection intervals:
3 min
5 min
8 min
10 min
48 hours
The mean becomes heavily distorted.
Track:
- mean;
- median;
- P90;
- P95;
- maximum.
This reveals whether AI is improving:
typical incidents
and:
long-tail failures.
Example AI Detection Scorecard
| Metric | Before AI | After AI |
|---|---|---|
| Median MTTD | 36 min | 21 min |
| P90 MTTD | 4.2 hrs | 2.8 hrs |
| Alert triage | 18 min | 7 min |
| Analyst override rate | — | 12% |
| False positive rate | 26% | 18% |
| External discovery | 19% | 13% |
These values are illustrative only.
Do not publish them as industry statistics.
The point is to measure AI against your own baseline.
Measure False Negatives Too
An AI tool may appear highly effective because it produces fewer false positives.
But what if it also misses more attacks?
Track:
- false positives;
- false negatives;
- analyst overrides;
- missed High/Critical incidents.
Detection quality requires both:
precision
and:
coverage.
AI and SOC Efficiency
AI should be judged by operational outcomes.
Useful metrics include:
- MTTD;
- MTTA;
- triage time;
- backlog age;
- MTTC;
- false-positive rate;
- analyst hours saved.
For the broader framework, see SOC Efficiency Metrics 2026.
Current Evidence: IBM 2026
IBM’s 2026 Cost of a Data Breach research provides useful evidence for AI/security automation.
IBM reports:
$4.99 million — global average breach cost.
56% — increase in AI-driven attacks.
$1.93 million — average cost savings associated with extensive use of AI and security automation compared with organizations using none.
These are strong statistics.
But they do not prove:
AI reduces MTTD by 50%.
Unless a study measures MTTD specifically, do not invent a detection-time percentage.
AI Is Improving Attacker Speed Too
IBM reports that AI is helping attackers:
- automate reconnaissance;
- generate phishing content;
- adapt malicious code;
- scale exploitation.
IBM says this can compress attack timelines from weeks toward hours.
This means defenders are not simply using AI for efficiency.
They are responding to a faster attack environment.
Current Evidence: Mandiant 2026
Mandiant’s M-Trends 2026 is based on more than 500,000 hours of frontline incident investigations conducted in 2025.
It reports:
- 14-day global median dwell time;
- some initial-access hand-offs in less than 30 seconds;
- greater use of AI by threat actors;
- persistent visibility problems on edge infrastructure.
This is exactly why detection programs need both:
speed
and:
coverage.
Current Evidence: Google Security Operations
Google announced new AI-driven security capabilities in 2026 designed to assist with monitoring, detecting, investigating, and containing AI-powered threats.
This supports real-world use cases such as:
- automated threat monitoring;
- investigation assistance;
- correlation;
- response support.
But vendor product capabilities should not be treated as independent proof of universal security outcomes.
Use them as examples of industry direction.
NIST and AI-Enabled Cyber Defense
NIST’s Cyber AI Profile work explicitly considers both:
- securing AI;
- using AI to enhance cybersecurity capabilities.
NIST’s preliminary Cyber AI Profile includes AI-related considerations within the DETECT function, including monitoring assets to identify anomalies and potentially adverse events.
NIST also released an initial public draft in August 2026 describing ways AI could assist organizations with Cybersecurity Framework 2.0 analysis and reporting.
These are useful governance references.
They should not be presented as proof that NIST endorses fully autonomous detection or containment.
AI in Zero Trust Environments
Your current article says AI “ensures continuous verification.”
I recommend changing that.
Zero Trust is a security architecture principle based on continuous evaluation of identity, device, access, and context.
AI can support Zero Trust by helping analyze:
- authentication behavior;
- device risk;
- session anomalies;
- access patterns.
But Zero Trust does not require AI.
A safer sentence is:
AI-assisted analytics can strengthen continuous access evaluation in Zero Trust environments by identifying unusual identity and device behavior.
AI Detection Risks
AI introduces its own security and operational risks.
1. False Positives
Normal activity is classified as malicious.
2. False Negatives
Real attacks are missed.
3. Model Drift
Detection quality changes as environments evolve.
4. Poor Training or Context
The model misunderstands legitimate activity.
5. Prompt Injection
Malicious content attempts to manipulate AI-enabled workflows.
6. Data Leakage
Sensitive security telemetry reaches inappropriate systems.
7. Hallucination
Generative systems produce unsupported conclusions.
8. Over-Automation
Organizations trust AI recommendations without verification.
NIST’s AI Risk Management Framework exists specifically to help organizations manage AI-related risks in a structured manner.
Human Validation Still Matters
AI can say:
“High probability of account takeover.”
The analyst should still ask:
- What evidence supports this?
- Is the user traveling?
- Is this a known automation account?
- Has the device changed legitimately?
- What business service is affected?
Security decisions should be evidence-driven.
AI Detection and Compliance Readiness
Faster detection can help compliance teams obtain facts earlier.
But detection metrics do not automatically start regulatory clocks.
For example:
SEC
The U.S. public-company incident disclosure timeline generally depends on materiality determination.
UK GDPR
The notification clock depends on awareness of a reportable personal-data breach.
Therefore:
AI alert ≠ automatic legal reporting trigger
AI can support:
- chronology;
- evidence gathering;
- classification;
- escalation.
Legal and privacy teams still determine legal obligations.
Detection Speed and SEC Reporting
Do not write:
Faster MTTD gives more time before the SEC four-day clock.
The relationship is more nuanced.
Better wording:
Faster detection can give management and legal teams earlier access to incident facts, which may support timely materiality assessment and disclosure readiness.
For details, see SEC Cyber Rule Timeline 2026.
AI Detection and UK Reporting
Similarly, AI may surface:
- personal-data exposure;
- unauthorized account activity;
- exfiltration indicators.
But the UK notification clock is tied to awareness of a reportable breach, not simply the first AI-generated alert.
For regulatory comparisons, see Cyber Incident Reporting Deadlines US vs UK.
How to Measure Whether AI Is Actually Improving Detection
Step 1: Establish a Baseline
Before deploying AI, record:
- median MTTD;
- mean MTTD;
- P90/P95;
- false positive rate;
- external discovery rate.
Step 2: Segment by Attack Type
Measure separately:
- ransomware;
- identity compromise;
- cloud compromise;
- malware;
- third-party incidents.
Step 3: Segment by Environment
Compare:
- endpoint;
- cloud;
- identity;
- network;
- SaaS;
- edge infrastructure.
Step 4: Measure Analyst Impact
Track:
- triage time;
- case workload;
- analyst overrides;
- investigation time.
Step 5: Measure Detection Quality
Track:
- missed incidents;
- false negatives;
- false positives;
- Critical detection coverage.
Step 6: Compare Trends
Example:
| KPI | Before | 90 days after |
|---|---|---|
| Median MTTD | 42 min | 29 min |
| P90 MTTD | 5.2 hrs | 3.1 hrs |
| Triage time | 18 min | 8 min |
| False positives | 28% | 21% |
| External discovery | 15% | 11% |
Again, illustrative.
Use your own data.
AI Detection Maturity Model
Level 1 — Rules Only
Static signatures and manual analysis.
Level 2 — Automated Enrichment
Security context gathered automatically.
Level 3 — Behavioral Analytics
Anomaly detection supplements rules.
Level 4 — AI-Assisted Correlation
Multiple signals combined automatically.
Level 5 — AI-Assisted Threat Hunting
Analysts use AI to search for hidden patterns.
Level 6 — Guardrailed Detection and Response
High-confidence detections trigger pre-approved workflows.
The goal should not automatically be:
maximum AI.
It should be:
appropriate automation with measurable improvement.
Common AI Detection Mistakes
1. Buying AI Before Fixing Telemetry
No data means poor detection.
2. Measuring Only Alert Volume
More alerts do not equal better detection.
3. Claiming AI Automatically Reduces Dwell Time
Measure it.
4. Ignoring False Negatives
Missing attacks matters more than reducing noise.
5. Using AI Output as Evidence
Preserve original logs.
6. Treating Vendor Claims as Universal Benchmarks
Validate in your environment.
7. Ignoring Identity and Cloud
Endpoint-only AI leaves blind spots.
8. Over-Automating Containment
Detection and response risk are different.
9. Confusing MTTD With Dwell Time
They are related but not identical.
10. Making Regulatory Decisions Automatically
AI should assist, not independently decide legal obligations.
Frequently Asked Questions
Can AI reduce breach detection time?
Yes, AI can help reduce detection time by improving behavioral analysis, alert correlation, prioritization, and investigation speed.
Actual performance depends on telemetry, implementation quality, attack type, and human workflow.
Does AI always reduce MTTD?
No.
If the environment has poor logging or visibility, AI may have insufficient evidence to detect the attack.
Can AI reduce dwell time?
Potentially.
Earlier detection can shorten attacker dwell time, but dwell-time reduction depends on whether AI can observe and recognize the relevant attacker behavior.
Does AI replace SIEM or EDR?
Generally no.
AI typically works on top of or alongside telemetry collected from systems such as SIEM, EDR, identity, and cloud platforms.
Does AI replace SOC analysts?
No.
AI can automate repetitive analysis and surface likely threats, while analysts still provide validation, context, investigation, and judgment.
What is the strongest current evidence for AI security benefits?
IBM’s 2026 Cost of a Data Breach research reports $1.93 million in average breach-cost savings associated with extensive use of AI and automation in security compared with organizations using none.
How fast are modern attackers moving?
Mandiant reports some initial-access hand-offs occurring in less than 30 seconds.
That does not mean every attack moves that quickly, but it demonstrates how compressed response windows can become.
What is the current global dwell-time statistic?
Mandiant reports a 14-day global median dwell time across its 2025 investigations.
It is a dataset-specific median, not a universal MTTD benchmark.
Does NIST support using AI in cybersecurity?
NIST is actively developing guidance around both cybersecurity of AI and AI-enabled cybersecurity. Its preliminary Cyber AI Profile includes considerations for AI-supported cyber defense and the Detect function.
Final Takeaway
AI can reduce breach detection time, but only when it improves a real detection capability.
The strongest use cases are:
behavioral analytics
identity anomaly detection
cross-source correlation
alert enrichment
AI-assisted triage
threat hunting
cloud detection
AI should be measured by outcomes such as:
lower median MTTD
lower P90/P95 MTTD
fewer externally discovered incidents
better Critical detection coverage
lower analyst triage time
—not simply by how many AI features a SOC deploys.
Current 2026 evidence supports a cautious but meaningful conclusion.
IBM shows strong economic benefits associated with extensive AI and security automation while simultaneously documenting rapidly increasing AI-enabled attack activity.
Mandiant shows that defenders face both stealthy intrusions lasting days or longer and attack hand-offs that can occur in seconds.
And NIST’s developing Cyber AI work recognizes AI as both a cybersecurity opportunity and a new area of risk that requires governance.
The useful question is therefore not:
“Do we use AI for cybersecurity?”
It is:
“Which threats does AI help us discover sooner, how much detection time does it actually save, and where do we still have blind spots?”
That is the measurement standard your 2026 detection strategy should use.
Recommended Links
Average Cyber Attack Detection Time 2026
Detection Speed Benchmarks by Industry