Board-Level Cybersecurity Metrics 2026: 10 KPIs Directors Should Track
Cybersecurity oversight is now an enterprise governance responsibility.
Boards do not need to become security operations teams, but they do need enough reliable information to understand whether cyber risk is:
- increasing or decreasing;
- aligned with business risk tolerance;
- being managed effectively;
- creating material financial or operational exposure;
- concentrated in critical suppliers;
- leaving important corrective actions unresolved.
That makes board-level cybersecurity metrics different from operational SOC metrics.
A SOC may need to know:
- alert queue age;
- endpoint isolation time;
- SIEM correlation quality;
- analyst case volume.
A board needs to know:
Are serious cyber risks being reduced, and where could a failure materially affect the business?
NIST Cybersecurity Framework 2.0 reinforces this distinction by adding Govern as a separate function, emphasizing risk-management strategy, roles, responsibilities, policy, oversight, and alignment with enterprise risk management.
For U.S. public companies, the SEC also requires annual disclosure regarding cybersecurity risk-management processes, management’s role, and the board’s oversight of cybersecurity risk.
A strong board dashboard therefore should not ask:
“How many alerts did the SOC close?”
It should ask:
“What cyber risks could materially affect the business, and are those risks being reduced?”
Board Cybersecurity Metrics at a Glance
| Board metric | What directors should ask |
|---|---|
| Material cyber incident trend | Are serious incidents increasing or decreasing? |
| Critical MTTD / MTTC trend | Are high-risk attacks being detected and contained faster? |
| External discovery rate | Are outsiders discovering major incidents before we do? |
| Business recovery time | How long are critical services disrupted? |
| KEV / critical vulnerability exposure | Are known exploited vulnerabilities still present? |
| Third-party cyber risk | Which suppliers create the greatest operational concentration risk? |
| Phishing-resistant MFA coverage | Are privileged and critical users strongly protected? |
| Regulatory reporting readiness | Can we classify and escalate reportable incidents on time? |
| Open high-risk exceptions | Which accepted risks remain unresolved? |
| Corrective-action closure | Are lessons learned and remediation commitments actually completed? |
These are not universal regulatory requirements. They are a practical governance framework for turning technical information into board-relevant risk indicators.
Table of Contents
What Makes a Cybersecurity Metric “Board-Level”?
A board metric should be:
- tied to business risk;
- trend-based;
- understandable without deep technical knowledge;
- connected to risk tolerance;
- actionable;
- comparable over time;
- focused on significant exposure.
A metric should help directors answer questions such as:
- Could this disrupt a critical business service?
- Could this create material financial loss?
- Is the organization becoming more resilient?
- Are serious vulnerabilities remaining open too long?
- Are important suppliers creating hidden dependency risk?
- Are previous incident lessons being implemented?
A metric that cannot support a governance decision probably belongs on an operational dashboard rather than a board dashboard.
Metric 1: Material Cyber Incident Trend
The board should understand the trend in significant or potentially material cyber incidents, not simply total alert volume.
Track incidents that caused or reasonably threatened:
- material financial impact;
- major operational disruption;
- sensitive-data exposure;
- critical-service interruption;
- significant customer harm;
- regulatory escalation.
A useful dashboard might show:
| Quarter | Critical incidents | Material / potentially material | Major service disruption |
|---|---|---|---|
| Q1 | 4 | 1 | 2 |
| Q2 | 3 | 0 | 1 |
| Q3 | 2 | 0 | 1 |
The board should focus on:
severity + business effect + trend
rather than raw incident count.
Why Raw Incident Count Can Mislead
Imagine:
Company A: 500 low-risk malware alerts, no serious incidents.
Company B: 20 incidents, including one major ransomware disruption.
The second company may have fewer incidents but significantly more business risk.
Board reporting should therefore weight:
- severity;
- operational effect;
- financial impact;
- recurrence.
Metric 2: Critical MTTD and MTTC Trend
Mean Time to Detect and Mean Time to Contain can be useful at board level when they are limited to high-severity incidents and presented as trends.
The board generally does not need:
“Enterprise MTTD is 27.4 minutes.”
It may need:
“Critical-incident median detection time decreased 31% over three quarters, but cloud incidents remain twice as slow to detect.”
That tells a risk story.
For definitions and formulas, see:
Use Median and Long-Tail Metrics
Do not show only averages.
A useful board view might include:
| Metric | Q1 | Q2 | Q3 |
|---|---|---|---|
| Critical median MTTD | 31 min | 22 min | 16 min |
| Critical P90 MTTD | 3.4 hrs | 2.5 hrs | 1.8 hrs |
| Critical median MTTC | 44 min | 31 min | 23 min |
This helps directors see whether:
- normal response is improving;
- a small number of incidents still take dangerously long.
For a broader metric comparison, see MTTD vs MTTR vs MTTC vs Dwell Time.
Metric 3: External Discovery Rate
One of the most revealing governance metrics is:
What percentage of major cyber incidents do we discover ourselves?
Mandiant’s M-Trends 2026 reports that across its 2025 investigations:
- 52% were first detected internally;
- 34% were first disclosed by an external entity;
- 14% were revealed by the adversary.
Those figures are dataset-specific, not universal targets.
But the concept is valuable.
Boards should track:
internal discovery
versus:
- supplier notification;
- customer notification;
- security researcher;
- law enforcement;
- attacker notification.
A high external-discovery rate may indicate:
- visibility gaps;
- weak monitoring;
- limited supplier oversight.
Metric 4: Business Recovery Time
Boards care about business interruption, not only containment.
Track the time required to restore:
- revenue-generating systems;
- customer-facing services;
- production;
- critical communications;
- essential operations.
A useful board metric is:
Critical Service Recovery Time
rather than vague “incident closure time.”
Example:
| Incident | Service affected | Outage | Recovery |
|---|---|---|---|
| Ransomware | Order processing | 11 hrs | Same day |
| Cloud failure | Customer portal | 3.2 hrs | Same day |
| Supplier breach | Shipping API | 19 hrs | Next day |
The board should ask:
Which business services have recovery times beyond our risk tolerance?
Recovery Time vs Incident Closure Time
These are not the same.
A service may be restored on Tuesday.
But:
- root cause may not be complete;
- regulators may still need updates;
- corrective actions may remain open.
Track separately:
business restored
and:
incident formally closed.
For the full operational lifecycle, see Cybersecurity Incident Response Timeline.
Metric 5: Known Exploited Vulnerability Exposure
A simple patch-speed average is often not the best board metric.
Boards should care more about:
Are vulnerabilities known to be actively exploited still present on critical assets?
CISA maintains the Known Exploited Vulnerabilities (KEV) Catalog as an authoritative source of vulnerabilities known to have been exploited in the wild and recommends organizations use it to help prioritize vulnerability remediation.
A useful board metric is:
Critical KEV Exposure
Track:
- number of KEVs present;
- number on internet-facing systems;
- number on critical assets;
- overdue KEVs;
- oldest unresolved KEV.
Example:
| Measure | Current |
|---|---|
| KEVs detected | 18 |
| On critical assets | 4 |
| Over internal SLA | 2 |
| Internet-facing | 1 |
This provides more business value than:
Average patch time = 18 days.
Add Vulnerability Remediation SLA Compliance
A useful companion metric is:
% of Critical / KEV vulnerabilities remediated within policy
Example:
93% within SLA
This helps the board determine whether remediation processes are functioning consistently.
Metric 6: Third-Party Cyber Risk
Boards should see cyber risk from important suppliers, not only internal systems.
Track high-risk third parties such as:
- cloud providers;
- MSPs;
- payment processors;
- critical SaaS platforms;
- logistics providers;
- identity providers.
Useful board measures include:
- number of critical suppliers;
- suppliers without current cyber assessment;
- suppliers with unresolved High/Critical findings;
- supplier incident notification time;
- concentration risk.
Supplier Concentration Matters
Consider:
40 critical business processes depend on one cloud or identity provider.
That is materially different from:
40 processes distributed across several suppliers.
A board-level dashboard should highlight concentration where a single cyber event could disrupt a large share of operations.
For operational supplier governance, see Third-Party Risk Assessment Checklist.
Metric 7: Phishing-Resistant MFA Coverage
Your current article uses phishing simulation failure rate as a primary board metric.
That can be useful, but it should not stand alone.
A stronger governance metric is:
phishing-resistant MFA coverage for privileged and critical users.
CISA’s Cybersecurity Performance Goals specifically recommend phishing-resistant MFA and rank hardware-based FIDO/WebAuthn or PKI approaches above weaker methods such as SMS.
Track:
- privileged-account coverage;
- remote-access coverage;
- executive-account coverage;
- critical administrator coverage.
Example:
| Account group | Phishing-resistant MFA |
|---|---|
| Privileged admins | 100% |
| Executives | 96% |
| Remote access users | 89% |
| General workforce | 72% |
The board should focus first on the highest-risk identities.
For deployment guidance, see Phishing-Resistant MFA Checklist.
Should Boards Still Track Phishing Simulation Failure Rate?
Yes—but as a supporting measure.
Instead of reporting only:
failure rate = 6%
show:
- trend over time;
- repeat-failure rate;
- high-risk department exposure;
- whether stronger technical controls are reducing dependency on user behavior.
Security should not rely solely on employees recognizing phishing.
Metric 8: Regulatory Reporting Readiness
Regulatory readiness should measure whether the organization can identify and escalate legal reporting obligations quickly.
This is not the same as:
MTTD
or:
MTTC.
For U.S. public companies, SEC Item 1.05 generally requires disclosure of a material cybersecurity incident within four business days after materiality is determined. The SEC also requires annual disclosure concerning board oversight and management’s role in cybersecurity risk.
A useful governance dashboard might track:
- time to legal escalation;
- time to materiality review;
- reportable-event classification accuracy;
- missed regulatory deadlines;
- tabletop performance.
Do Not Treat Operational Metrics as Legal Clocks
Do not tell the board:
“Our MTTD automatically starts the SEC four-day deadline.”
That is incorrect.
Different laws use different trigger points.
For the detailed comparison, see Cyber Incident Reporting Deadlines: US vs UK.
CIRCIA Should Be Presented as Readiness, Not Current Mandatory Reporting
Your current article says CIRCIA reinforces present accountability.
Be more precise.
Where CIRCIA reporting requirements are not yet in force, the board should monitor:
CIRCIA readiness
rather than treating the statutory 72-hour framework as a currently active reporting deadline for all covered entities.
This prevents the article from overstating current obligations.
Metric 9: Open High-Risk Exceptions
Cyber programs always have unresolved risk.
The board should know:
Which significant risks have management accepted or deferred?
Examples include:
- unsupported critical system;
- delayed MFA deployment;
- unpatched internet-facing device;
- supplier with unresolved control failure;
- expired disaster-recovery test;
- critical logging gap.
Track:
| Risk | Age | Owner | Target closure |
|---|---|---|---|
| Legacy VPN exposure | 72 days | CIO | Q4 |
| Supplier MFA gap | 41 days | Procurement | Oct |
| Cloud logging gap | 18 days | CISO | Sept |
The board should ask:
Is management consciously accepting these risks, or have they simply been left unresolved?
Risk Acceptance Should Be Explicit
A mature governance process records:
- risk;
- business impact;
- compensating control;
- executive owner;
- acceptance date;
- review date.
This supports NIST CSF 2.0’s emphasis on governance, risk tolerance and defined responsibility.
Metric 10: Corrective-Action Closure
After major:
- incidents;
- audits;
- penetration tests;
- risk assessments;
- regulator findings,
the organization creates corrective actions.
The board should track whether those commitments are actually completed.
Useful measures:
- open Critical actions;
- overdue actions;
- oldest action;
- repeat findings;
- closure rate.
Example:
| Measure | Current |
|---|---|
| High-risk corrective actions | 14 |
| Overdue | 3 |
| >90 days old | 2 |
| Repeat findings | 1 |
This tells the board whether cybersecurity improvement is happening after problems are identified.
Repeat Findings Are Especially Important
If the same control weakness appears repeatedly in:
- incident reviews;
- audits;
- penetration tests,
that may indicate a governance problem rather than a technical one.
Boards should ask:
Why has management failed to correct a known recurring weakness?
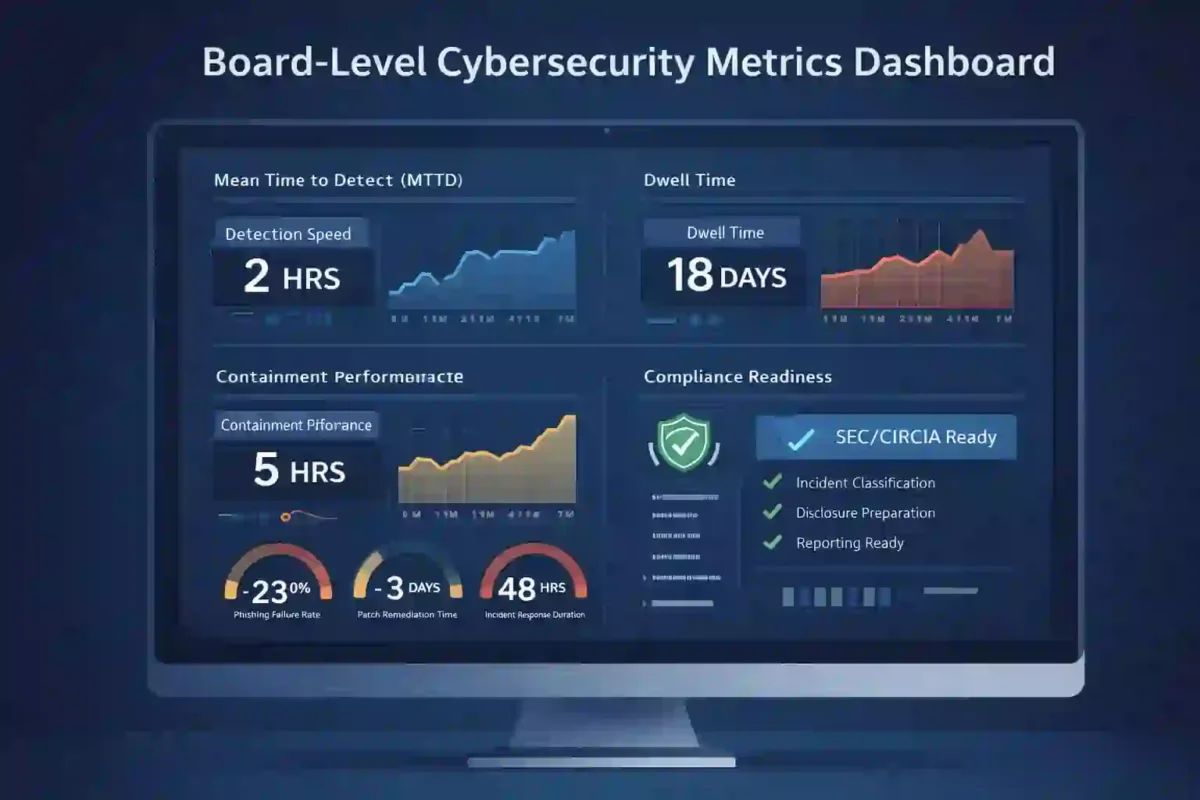
Cybersecurity Time Board Dashboard Example
A practical quarterly dashboard could look like this:
| Board KPI | Current | Previous | Status |
|---|---|---|---|
| Material / major cyber incidents | 1 | 2 | Improving |
| Critical median MTTD | 16 min | 22 min | Improving |
| Critical median MTTC | 23 min | 31 min | Improving |
| Externally discovered serious incidents | 12% | 18% | Improving |
| Critical service recovery | 6.4 hrs | 8.1 hrs | Improving |
| KEVs over SLA | 2 | 5 | Improving |
| Privileged phishing-resistant MFA | 100% | 92% | Improved |
| Critical suppliers with unresolved High risk | 3 | 4 | Improving |
| Regulatory deadlines missed | 0 | 0 | Stable |
| Overdue High-risk corrective actions | 3 | 5 | Improving |
These numbers are illustrative, not universal benchmarks.
Add Risk Tolerance to the Dashboard
Every metric should have context.
Instead of:
Recovery time = 6 hours
show:
Recovery time = 6 hours
Board-approved tolerance = 4 hours
Status = above tolerance
That transforms an operational statistic into a governance indicator.
Board Metrics Should Show Trends
One isolated number rarely tells the board enough.
Prefer:
Current quarter
Previous quarter
12-month trend
Risk tolerance
Management action
This format answers:
- Where are we now?
- Are we improving?
- Are we outside tolerance?
- What is management doing?
What the SEC Actually Requires
For public companies subject to the SEC’s cyber disclosure rules, annual disclosures include information about:
- cybersecurity risk-management processes;
- management’s role in assessing and managing material cyber risks;
- board oversight of cybersecurity risk.
The SEC does not mandate:
- a particular cyber committee;
- a specific MTTD;
- a specific MTTC;
- a required board KPI dashboard.
Your article should therefore say:
These metrics may help boards perform oversight and management demonstrate structured governance.
Not:
The SEC requires boards to track these metrics.
That distinction improves accuracy.
NIST CSF 2.0 and Board Governance
NIST CSF 2.0 introduced Govern as a distinct function because cybersecurity governance needed greater visibility.
NIST says the function helps align cybersecurity with:
- enterprise risk management;
- legal obligations;
- roles and responsibilities;
- policies;
- risk tolerance.
This makes CSF 2.0 particularly useful for board discussions.
NIST Cybersecurity Framework 2.0
CISA Performance Goals and Measurable Outcomes
CISA’s Cross-Sector Cybersecurity Performance Goals are voluntary high-impact security practices designed to help organizations prioritize investments and measure cybersecurity maturity. CISA explicitly describes them as measurable practices that can be tailored to an organization’s risks and maturity.
Useful board-relevant areas include:
- MFA;
- vulnerability remediation;
- logging;
- incident response;
- recovery.
CISA Cross-Sector Cybersecurity Performance Goals
Board Metrics vs SOC Metrics
| SOC dashboard | Board dashboard |
|---|---|
| Alert count | Material incident trend |
| Individual analyst workload | Critical response trend |
| SIEM rule performance | Business recovery exposure |
| False-positive details | Significant visibility gaps |
| Endpoint isolation actions | Critical MTTC |
| Raw vulnerabilities | KEV / critical exposure |
| Ticket backlog | Overdue risk remediation |
| Tool automation | Business-risk reduction |
Both dashboards matter.
But they serve different audiences.
For operational metrics, see SOC Efficiency Metrics 2026.
Avoid Cybersecurity Vanity Metrics
Boards should be cautious with measurements such as:
- number of blocked attacks;
- total firewall events;
- total phishing emails blocked;
- total security tools deployed.
Large numbers often look impressive without revealing actual risk.
For example:
“We blocked 4.2 million malicious requests.”
The board still does not know:
- whether important attacks succeeded;
- whether critical systems are resilient;
- whether major vulnerabilities remain unresolved.
Useful Board Question: “So What?”
For every metric, ask:
So what?
Example:
24 critical vulnerabilities.
So what?
Better:
24 critical vulnerabilities, including three KEVs on externally reachable systems. Two are beyond policy SLA.
Now the board can understand the risk.
Add Financial and Operational Context
Where reliable estimates exist, translate technical metrics into business effect.
Examples:
- hours of customer-facing downtime;
- revenue at risk;
- production loss;
- remediation cost;
- critical service dependency;
- cyber insurance retention.
Do not invent precise financial numbers when they are uncertain.
Use ranges or scenarios where appropriate.
Third-Party Concentration Dashboard
A useful board view can show:
| Supplier | Critical services dependent | Risk status |
|---|---|---|
| Cloud Provider A | 12 | Moderate |
| Identity Provider B | 9 | High |
| Payment Provider C | 5 | Moderate |
The goal is not to micromanage suppliers.
It is to identify systemic dependency.
Board-Level Regulatory Readiness Table
| Regime | Board-relevant question |
|---|---|
| SEC | Can materiality be assessed without unreasonable delay? |
| UK GDPR | Can reportable personal-data breaches be identified quickly? |
| DORA | Are major ICT incidents classified and escalated? |
| NIS2 | Are significant incidents identified and reported appropriately? |
| CIRCIA readiness | Are covered-event processes prepared for future mandatory reporting? |
This keeps legal trigger analysis separate from operational performance.
How Often Should Boards Review Cybersecurity Metrics?
There is no universal frequency.
A practical model might be:
Quarterly
- major incident trend;
- MTTD/MTTC trends;
- recovery;
- KEV exposure;
- supplier risk;
- MFA coverage;
- high-risk exceptions.
Immediately / ad hoc
For:
- potentially material cyber incident;
- major business disruption;
- significant third-party breach;
- major regulatory issue.
Annually
Review:
- cyber risk tolerance;
- governance structure;
- major investments;
- strategic cyber risk.
Questions Directors Should Ask Management
A board can use questions such as:
- Which cyber scenario creates the largest business interruption risk?
- Which critical vulnerabilities remain unresolved?
- Are serious incidents being detected internally?
- How long does it take to restore our most important services?
- Which third parties create concentration risk?
- Are privileged identities protected with phishing-resistant MFA?
- Which cyber risks are above our approved tolerance?
- Which corrective actions are overdue?
- Have any major incidents repeated a previously known weakness?
- Can management meet applicable reporting obligations?
These questions create better oversight than asking:
“Are we secure?”
Common Board Reporting Mistakes
1. Showing Too Many Technical Metrics
Boards need decision-relevant information.
2. Reporting Without Risk Tolerance
A number has little meaning without context.
3. Using Only Green Status Indicators
Cybersecurity is not binary.
Show uncertainty and exceptions.
4. Hiding Long-Tail Incidents
Use P90/P95 where relevant.
5. Treating Compliance as Security
Compliance does not guarantee resilience.
6. Treating SOC Metrics as Regulatory Requirements
MTTD and MTTC can support governance but are not mandated SEC metrics.
7. Ignoring Third Parties
Supplier concentration can create material business exposure.
8. Focusing Only on Phishing Training
Technical protections such as phishing-resistant MFA often reduce risk more directly than awareness scores alone. CISA specifically recommends phishing-resistant MFA as a high-impact security measure.
9. Tracking Vulnerability Counts Without Exploit Context
Use KEV and asset criticality to prioritize.
10. Failing to Track Corrective Actions
Unresolved repeat findings are a governance warning.
Frequently Asked Questions
What cybersecurity metrics should boards track?
A useful board dashboard can include:
- major incident trends;
- critical detection/containment time;
- external discovery;
- recovery time;
- KEV exposure;
- supplier risk;
- strong-authentication coverage;
- regulatory readiness;
- high-risk exceptions;
- corrective-action closure.
Does the SEC require boards to track MTTD or MTTC?
No.
The SEC requires relevant disclosure concerning board oversight, management’s role, and cybersecurity risk-management processes, but it does not prescribe MTTD or MTTC as mandatory board KPIs.
Does the SEC require cybersecurity expertise on the board?
The adopted SEC rule does not impose a mandatory cybersecurity-expertise requirement for board members. The focus is on disclosure of board oversight and management’s role.
Why is NIST CSF 2.0 useful for boards?
NIST CSF 2.0 explicitly elevates governance and helps align cybersecurity risk with enterprise risk management, risk tolerance, policy and accountability.
What is KEV exposure?
It measures organizational exposure to vulnerabilities in CISA’s Known Exploited Vulnerabilities Catalog—vulnerabilities known to have been exploited in the wild. CISA recommends using KEV as an input to vulnerability prioritization.
Should boards track phishing failure rates?
They can, but the measure should not stand alone.
Pair it with stronger control metrics such as phishing-resistant MFA coverage and repeat-failure trends.
Should boards track dwell time?
Dwell time can be useful as a trend or major-incident indicator, but external research should not be treated as a universal benchmark.
Mandiant reported a 14-day global median dwell time across its 2025 investigations in M-Trends 2026.
What percentage of breaches are detected internally?
There is no universal figure.
In Mandiant’s 2025 investigation dataset, 52% were first detected internally.
How often should cybersecurity metrics go to the board?
Frequency should reflect risk and governance needs. Quarterly reporting is common as an operating model, with immediate escalation for significant incidents and annual strategic review.
Final Takeaway
A board-level cybersecurity metrics program should not turn directors into SOC analysts.
Its purpose is to translate technical security performance into:
- enterprise risk;
- business interruption;
- financial exposure;
- regulatory readiness;
- resilience;
- accountability.
The strongest 2026 board dashboard does not simply show:
MTTD
MTTC
phishing score
It shows:
Are major incidents getting worse or better?
Can we recover critical services within our tolerance?
Are known exploited vulnerabilities still exposed?
Are important suppliers increasing concentration risk?
Are privileged identities strongly protected?
Are high-risk exceptions and corrective actions being closed?
NIST CSF 2.0 supports this governance-centered approach by placing Govern alongside Identify, Protect, Detect, Respond and Recover and aligning cybersecurity with enterprise risk management.
The SEC likewise focuses on meaningful disclosure about cybersecurity risk management, management responsibilities and board oversight—not on prescribing a universal technical scorecard.
The most useful board question is therefore not:
“How many cyber attacks did we block?”
It is:
“Which cyber risks remain capable of materially disrupting the business, and is management reducing those risks fast enough?”
That is what effective cyber governance should reveal.
Recommended Links
Use these naturally:
[Board-Level Cybersecurity Metrics Guide — current page] — do not self-link repeatedly.
MTTD vs MTTR vs MTTC vs Dwell Time
SEC Cyber Incident Disclosure Checklist