Data Breach Timeline Template 2026: Incident Chronology, Evidence and Reporting Log
A serious cybersecurity incident rarely begins with a complete picture.
More often, it starts with fragments:
- an unusual security alert;
- a user complaint;
- a vendor warning;
- a suspicious administrator login;
- an unexpected data transfer;
- a service outage;
- activity that only becomes meaningful after investigators correlate several events.
During the first hours, the biggest problem is often not lack of effort.
It is lack of shared chronology.
Security may be investigating one timeline. Legal may be trying to establish when the company became aware of a breach. Privacy teams may be calculating notification deadlines. Executives may be making business decisions based on incomplete information. Vendors may be supplying new facts later.
A well-designed data breach timeline template gives all of those teams one authoritative record.
It should show:
what happened → when it happened → what was known → who decided → what action followed
NIST’s current incident-response guidance emphasizes integrating preparation, detection, response and recovery across the organization rather than treating incident handling as an isolated technical activity.
For regulated organizations, a timeline also becomes essential because different legal obligations use different trigger points.
For example:
- SEC disclosure can depend on the time materiality is determined;
- UK GDPR reporting depends on awareness of a reportable personal data breach;
- other regimes may depend on incident classification, reasonable belief, ransom payment, or restoration milestones.
A useful timeline should therefore record regulatory decision points separately from technical events.
Data Breach Timeline at a Glance
| Timeline event | Why it matters |
|---|---|
| First suspicious activity | Establishes possible attack window |
| First security alert | Records technical detection |
| Incident validated | Shows when the event became credible |
| Incident owner assigned | Establishes accountability |
| Evidence preserved | Supports forensic integrity |
| Containment started | Records response action |
| Personal-data breach awareness | May trigger privacy reporting |
| Materiality review started | Supports SEC governance |
| Materiality determined | May start SEC Form 8-K clock |
| Regulator notification | Demonstrates compliance timing |
| Customer notification | Records communications |
| Recovery completed | Shows operational restoration |
| Root cause confirmed | Supports final analysis |
| Incident closed | Defines end of response lifecycle |
The most important principle is:
Do not collapse all of these events into one “incident date.”
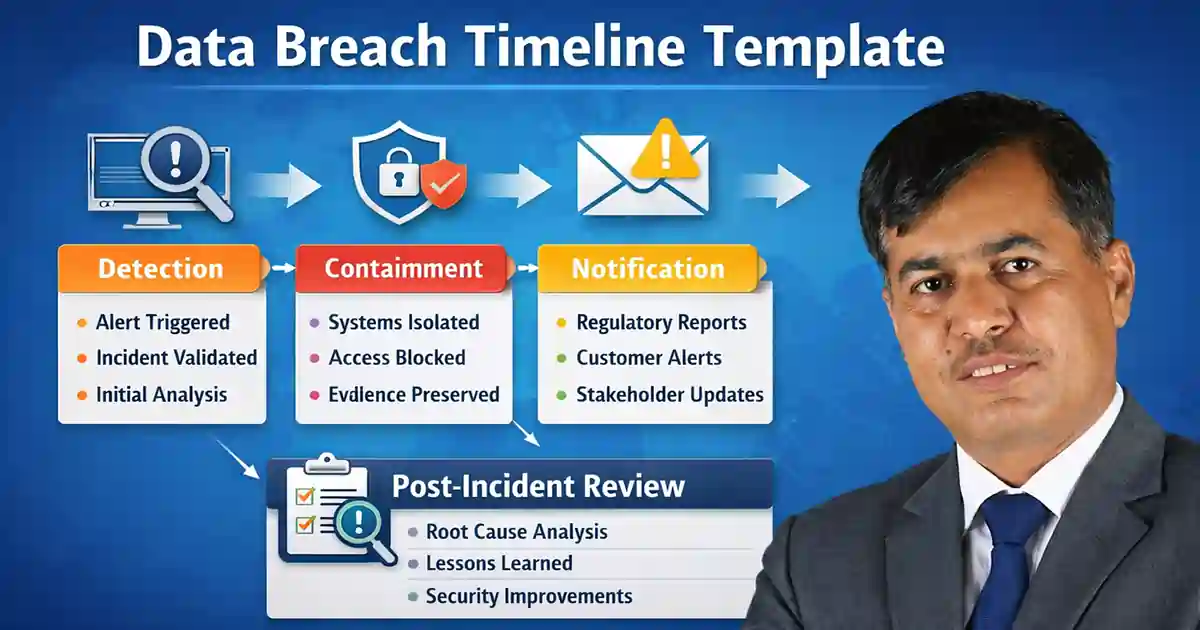
Table of Contents
Why a Data Breach Timeline Matters
A timeline serves several purposes simultaneously.
Operational coordination
It helps responders understand:
- what happened;
- what actions have already been taken;
- what still needs to happen;
- which facts are confirmed;
- which facts remain uncertain.
Legal and compliance analysis
It can help establish:
- when the organization became aware of a breach;
- when a materiality determination was made;
- when a regulatory reporting threshold was met;
- whether notification deadlines were satisfied.
Executive decision-making
Leadership can understand the event without reconstructing it from separate security, legal and IT notes.
Evidence preservation
The organization can show why decisions were made based on the information available at the time.
Post-incident review
The timeline exposes:
- delayed escalation;
- weak logging;
- vendor notification problems;
- containment delays;
- reporting bottlenecks.
Your current article already captures this concept well, but the rewritten version should make the timeline much more explicitly regulatory-trigger aware.
A Data Breach Timeline Is Not the Same as a Forensic Timeline
These two records overlap, but they serve different purposes.
Forensic timeline
Focuses heavily on technical activity:
- attacker login;
- process execution;
- persistence;
- lateral movement;
- privilege escalation;
- data access;
- exfiltration.
Incident-response timeline
Adds operational and governance events:
- detection;
- escalation;
- legal review;
- containment;
- regulator notification;
- customer communication;
- recovery;
- management decisions.
The strongest incident record may combine both, but the company should understand the distinction.
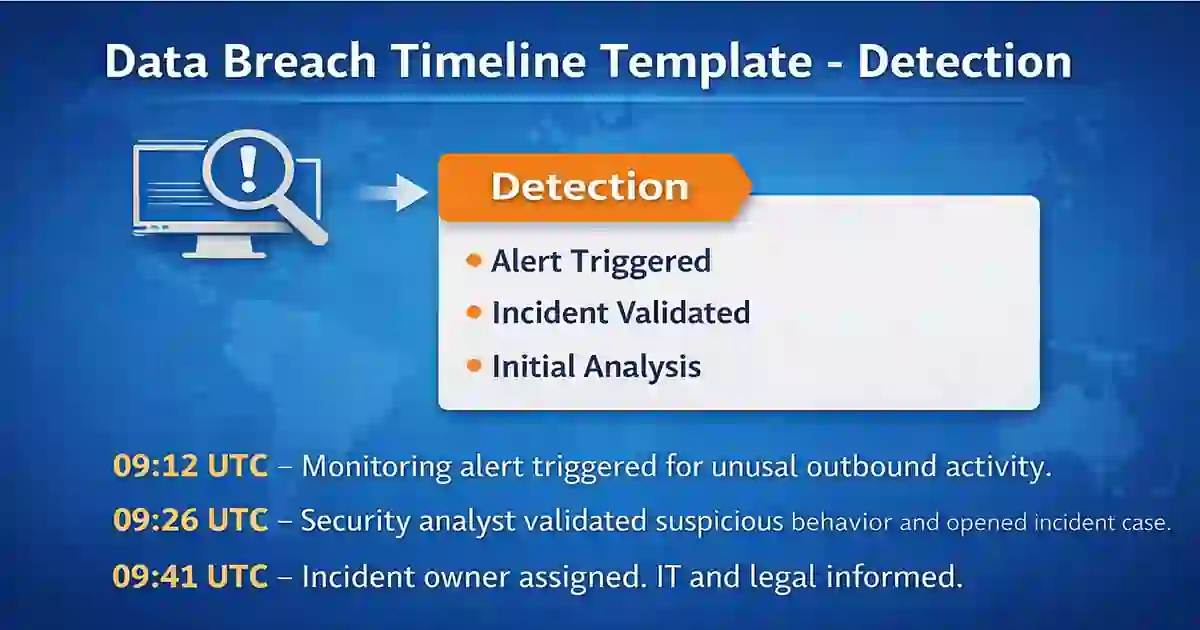
A useful timeline can be organized into seven phases:
Detection
Validation
Containment
Assessment
Regulatory and stakeholder notification
Recovery
Post-incident review
Each phase should include:
timestamp;
event;
source;
owner;
evidence;
decision;
confidence level;
next action.
Recommended Timeline Fields
Field
Example
Date/time
09 Sep 2026, 09:12 UTC
Event
Suspicious outbound transfer detected
Source
EDR / SIEM
Owner
SOC analyst
Status
Confirmed / suspected
Evidence
Alert ID 49382
Decision
Escalate to IR
Regulatory relevance
None yet
Next action
Preserve logs
This structure is much more useful than recording only narrative notes.
Phase 1: Detection
Detection begins when something suggests that unauthorized activity may be occurring.
Possible sources include:
- SIEM alerts;
- EDR;
- IDS/IPS;
- cloud audit logs;
- user reports;
- vendor notifications;
- law-enforcement contact;
- customer complaints;
- threat-intelligence alerts.
The objective at this stage is not to prove the entire breach.
It is to preserve the first reliable observations.
NIST SP 800-61 Rev. 3 emphasizes improving incident detection and response as part of broader cybersecurity risk management.
Record during detection
- exact first observed time;
- time alert was reviewed;
- alert source;
- analyst;
- affected account/system;
- initial severity;
- indicators of compromise;
- evidence location;
- whether personal data may be involved.
Example
09:12 UTC — SIEM triggered unusual outbound-transfer alert from internal repository.
09:26 UTC — Analyst confirmed activity was inconsistent with normal user behavior.
09:41 UTC — Incident record IR-2026-014 opened and incident-response lead assigned.
Phase 2: Validation and Confirmation
Detection does not automatically mean a breach has occurred.
The next phase should distinguish:
- false positive;
- suspicious event;
- confirmed security incident;
- confirmed data breach.
That distinction matters because regulatory clocks may depend on a later level of certainty rather than the first technical alert.
Record
- time incident was validated;
- evidence supporting validation;
- affected systems;
- suspected attack vector;
- current confidence;
- who approved escalation.
Example
10:18 UTC — Investigation confirmed unauthorized use of privileged credentials.
10:42 UTC — Incident severity raised from Medium to High.
10:55 UTC — Legal, privacy and executive incident contacts notified.
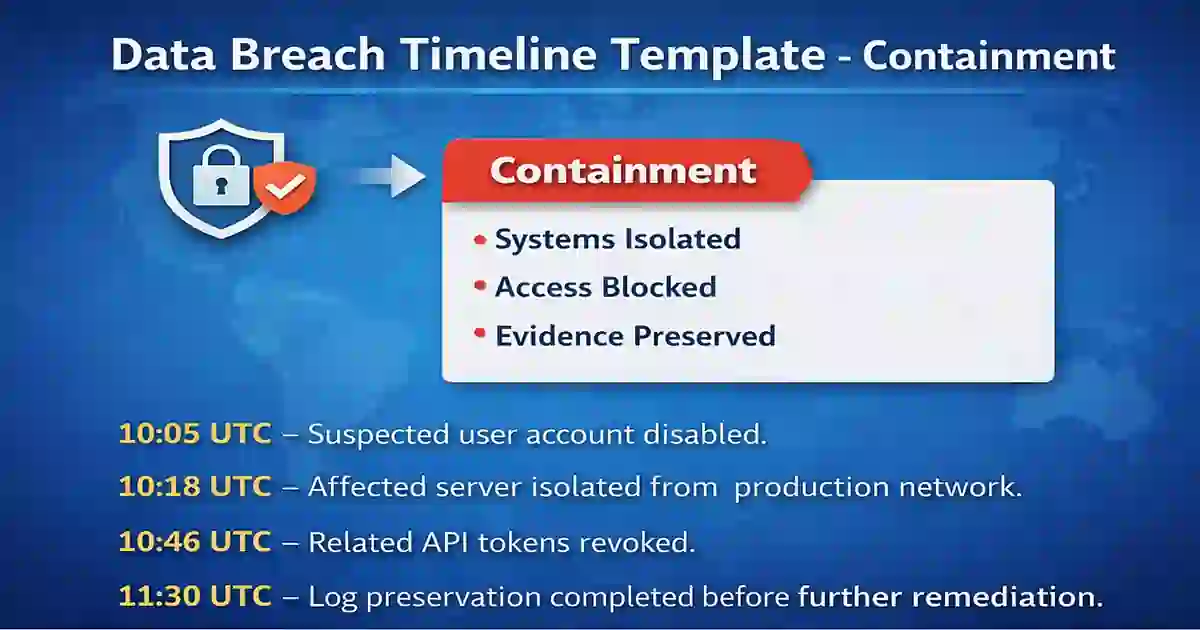
Phase 3: Containment
Containment aims to stop further harm while preserving evidence.
Possible actions include:
- disable accounts;
- revoke sessions;
- isolate hosts;
- block IP addresses;
- disable integrations;
- restrict cloud access;
- rotate tokens;
- suspend compromised applications.
Your current article correctly stresses that quick action should not destroy the evidence needed for later reconstruction.
What to record
- containment action;
- exact time;
- person approving it;
- system affected;
- evidence preserved beforehand;
- operational impact;
- result.
Example
11:05 UTC — Compromised administrator account disabled.
11:18 UTC — Production host isolated.
11:32 UTC — Active sessions revoked.
11:44 UTC — Cloud API keys rotated.
For identity-related containment, see Phishing-Resistant MFA Checklist and Info Stealer Malware in 2026.
Phase 4: Scope and Impact Assessment
Once immediate containment is underway, investigators need to understand the real scope.
Questions include:
- Which systems were accessed?
- What data was exposed?
- Was information copied or only viewed?
- How long did access persist?
- Which business functions were affected?
- Which customers may be affected?
- Which jurisdictions apply?
- Was a supplier involved?
This phase often changes earlier assumptions.
A strong timeline should preserve those changes rather than overwrite the old understanding.
Record
- confirmed systems;
- suspected systems;
- attack window;
- data categories;
- number of individuals;
- number of records;
- business impact;
- service downtime;
- geographic/jurisdictional impact;
- supplier involvement.
Example
15:20 UTC — Initial review indicates unauthorized access to document repository.
18:40 UTC — Customer contact information may have been accessed.
Day 2, 09:10 UTC — Cloud audit logs confirm access to 4,820 records.
Day 2, 11:45 UTC — No evidence yet of payment-card data access.
Record Confidence Levels
One improvement I strongly recommend is adding a confidence field.
For example:
| Finding | Confidence |
|---|---|
| Unauthorized access confirmed | High |
| Customer data exfiltrated | Medium |
| Privileged credential compromised | High |
| Attacker entered through VPN | Low/under investigation |
This prevents later readers from treating early assumptions as confirmed facts.
Phase 5: Regulatory Trigger Tracking
This is the biggest improvement I recommend over your current article.
Do not record only:
“Legal notified.”
Record the specific trigger timestamp for each relevant regulation.
Different regimes use different concepts.
SEC Materiality Timestamp
For U.S. public companies, the SEC generally requires Form 8-K Item 1.05 within four business days after the company determines the cybersecurity incident is material. The deadline is not tied directly to discovery, and the materiality determination must be made without unreasonable delay.
Record:
- materiality review started;
- participants;
- facts considered;
- decision;
- exact determination time.
Example
Day 2, 14:30 UTC — Disclosure committee determines incident is material. SEC Item 1.05 filing clock recorded.
For the full process, see SEC Cyber Incident Disclosure Checklist.
UK GDPR Awareness Timestamp
The ICO requires notification of certain personal data breaches within 72 hours of becoming aware of the breach, where feasible. The ICO also says organizations should record all personal data breaches, even when notification is not required.
Record:
- when reasonable certainty of a personal data breach was established;
- risk assessment;
- whether reporting was required;
- reporting decision.
Example
Day 1, 17:10 UTC — Privacy team determines there is sufficient certainty that personal information was accessed. UK GDPR awareness time recorded.
For a comparison of reporting clocks, see Cyber Incident Reporting Deadlines 2026: US vs UK.
CIRCIA Trigger Timestamp
If CIRCIA becomes applicable to the organization once the mandatory rule is effective, the incident record should separately track the event that starts the federal CIRCIA reporting workflow.
Your timeline should not assume that:
detection = CIRCIA trigger = SEC materiality = UK GDPR awareness.
Those can all be different times.
See CIRCIA 2026 Reporting Readiness.
DORA, NIS2 and CRA Clocks
For multinational organizations, a single incident may trigger EU regulatory timelines as well.
Your timeline should be capable of recording:
- DORA classification;
- NIS2 awareness;
- CRA reporting decision;
- regulator submission time.
Do not create separate chronologies for each regulation if one authoritative master timeline can support all of them.
Relevant internal guides:
Cybersecurity Time Regulatory Trigger Table
| Regime | Record this timestamp |
|---|---|
| SEC | Materiality determination |
| UK GDPR | Awareness of reportable personal-data breach |
| CIRCIA | Covered-incident trigger under applicable final framework |
| DORA | Incident awareness + major classification |
| NIS2 | Awareness of significant incident |
| CRA | Awareness of reportable vulnerability/severe incident |
| Contract | When contractual notification duty is triggered |
This table gives the article much more original practical value.
Phase 6: Notification
Notification is not one event.
It may include:
- regulator notice;
- customer communication;
- employee notice;
- insurer notice;
- law-enforcement contact;
- board notification;
- supplier escalation.
The timeline should show each separately.
Record
- notification type;
- recipient;
- required deadline;
- actual submission time;
- confirmation/reference number;
- approved wording;
- responsible person;
- follow-up due date.
Example
Day 3, 08:05 UTC — ICO notification submitted. Reference ICO-XXXXX.
Day 3, 11:20 UTC — Cyber insurer notified.
Day 3, 13:15 UTC — Customer notification distributed.
Day 3, 16:45 UTC — Board incident update completed.
Report Early, Update Later Where Permitted
Organizations should not always wait until the investigation is complete.
The ICO explicitly says an organization should report within 72 hours where required even if it does not yet have all details and then provide further information without undue delay.
Similarly, SEC rules recognize that a company may not know every required fact when the initial Item 1.05 filing is due and provide a mechanism for later disclosure.
That means the incident timeline should clearly distinguish:
- initial notification;
- supplemental notification;
- amendment;
- final report.
Phase 7: Recovery
Recovery is more than turning services back on.
The organization should confirm:
- the attack path is closed;
- compromised credentials are rotated;
- affected systems are clean;
- patches are applied;
- backups are validated;
- monitoring is increased;
- business owners approve restoration.
Record
- restoration time;
- system;
- backup source;
- security changes;
- validation;
- business approval;
- remaining risks.
Example
Day 4, 11:00 UTC — Repository restored from verified backup.
Day 4, 16:45 UTC — Privileged MFA enforcement completed.
Day 5, 10:30 UTC — Enhanced monitoring deployed.
Day 5, 14:20 UTC — Business owner approved return to service.
For remediation governance, see Patch Management SLA Template.
Recovery Does Not Mean Incident Closure
A system may be operational again while several issues remain unresolved:
- data-exposure analysis;
- customer notification;
- regulatory updates;
- root-cause investigation;
- litigation hold;
- supplier review.
Therefore record separately:
service restored
and:
incident formally closed.
Phase 8: Root Cause and Post-Incident Review
NIST SP 800-61 Rev. 3 emphasizes continuous improvement as part of incident-response maturity.
Your timeline should ultimately capture:
- root cause;
- control failure;
- response gaps;
- reporting delays;
- supplier failures;
- lessons learned;
- remediation actions;
- accountable owners;
- due dates.
Example
Day 8 — Root cause confirmed: compromised third-party VPN credential.
Day 9 — Management approves MFA enforcement and VPN segmentation remediation plan.
Day 30 — Post-incident review completed.
Day 45 — Final remediation verification complete.
Master Data Breach Timeline Template
This is the copy-and-use version I recommend putting in the article.
Incident Details
- Incident ID:
- Date opened:
- Incident commander:
- Business unit:
- Severity:
- Primary systems:
- Jurisdictions:
- Outside counsel:
- Forensics provider:
- Insurer:
Chronology Log
| Date/time | Event | Source | Owner | Confidence | Regulatory relevance | Action |
|---|---|---|---|---|---|---|
Use UTC consistently unless there is a specific reason not to.
Detection
- First suspicious activity:
- First security alert:
- Alert source:
- First analyst review:
- Incident validation time:
- Evidence preserved:
- Indicators of compromise:
Containment
- Accounts disabled:
- Sessions revoked:
- Systems isolated:
- Network blocks:
- API keys rotated:
- Vendor access restricted:
- Evidence preserved before remediation:
Scope Assessment
- Systems affected:
- Accounts affected:
- Attack window:
- Data categories:
- Records/users affected:
- Exfiltration confirmed:
- Operational impact:
- Service downtime:
- Suppliers involved:
Regulatory Trigger Record
SEC
- Materiality review started:
- Materiality determined:
- Decision owner:
- Filing deadline:
- Form 8-K filed:
- Amendment required:
UK GDPR
- Personal data breach confirmed:
- Awareness time:
- Risk assessment:
- ICO notification required:
- ICO notified:
- Individuals notified:
Other Regimes
- CIRCIA trigger:
- DORA trigger:
- NIS2 trigger:
- CRA trigger:
- Sector regulator:
- Contractual notification:
Stakeholder Notification
- Board notified:
- Customers notified:
- Employees notified:
- Insurer notified:
- Law enforcement notified:
- Vendor notified:
- Regulator reference numbers:
Recovery
- Systems restored:
- Credentials rotated:
- Security fixes:
- Monitoring changes:
- Backup validation:
- Business return-to-service approval:
- Residual risks:
Post-Incident
- Root cause:
- Control gaps:
- Vendor gaps:
- Reporting delays:
- Lessons learned:
- Corrective actions:
- Owners:
- Due dates:
- Closure date:
Example Completed Timeline
| Time | Event | Significance |
|---|---|---|
| 09:12 | SIEM detects unusual outbound traffic | Detection |
| 09:26 | Analyst validates suspicious behavior | Incident validation |
| 09:41 | Incident owner assigned | Governance |
| 10:05 | User account disabled | Containment |
| 10:18 | Server isolated | Containment |
| 12:20 | Personal data potentially affected | Privacy escalation |
| 15:20 | Unauthorized repository access confirmed | Scope |
| 17:10 | Personal data breach awareness established | UK GDPR clock |
| Day 2 09:10 | 4,820 records confirmed affected | Scope update |
| Day 2 14:30 | Incident determined material | SEC clock |
| Day 3 08:05 | ICO notification submitted | Regulatory |
| Day 3 11:00 | Form 8-K drafting completed | SEC |
| Day 4 11:00 | System restored | Recovery |
| Day 8 | Root cause confirmed | Investigation |
| Day 30 | Post-incident review completed | Closure |
This is illustrative and not a legal deadline calculator.
Common Timeline Mistakes
1. Recording Only the Attack Date
A regulatory timeline needs more than:
Breach occurred 9 September.
Record all major decision points.
2. Reconstructing the Timeline After the Incident
Your current article correctly warns against reconstructing events from memory.
Update the timeline in real time.
3. Overwriting Earlier Assumptions
Do not erase:
“Exfiltration suspected.”
when later evidence says:
“Exfiltration confirmed.”
Keep both entries with timestamps.
4. Mixing Time Zones
Use one standard, preferably UTC, and display local time separately when needed.
5. Recording Actions Without Owners
“Account disabled” is less useful than:
11:05 UTC — Identity administrator J.S. disabled account after IR approval.
6. Missing Regulatory Trigger Times
Record:
- awareness;
- materiality;
- classification;
- payment;
- notification.
These may drive legal deadlines.
7. Failing to Record Unknowns
Unknown information is part of the incident state.
Use:
- confirmed;
- probable;
- suspected;
- unknown.
8. Treating the Timeline as a Security-Only Document
Legal, privacy, finance, communications and business teams should contribute.
Timeline Evidence Preservation
The chronology should point to evidence, not attempt to contain all evidence itself.
Example:
12:14 UTC — Suspicious OAuth token confirmed. Evidence: Entra sign-in export EV-018.
Evidence may include:
- EDR logs;
- cloud audit logs;
- email headers;
- screenshots;
- forensic images;
- packet captures;
- regulator receipts;
- call notes.
Keep the incident timeline as an index into evidence.
Vendor Events Should Be Recorded Too
If a supplier is involved, record:
- when the supplier first detected the incident;
- when it notified you;
- what it initially said;
- what facts changed later;
- what logs it provided;
- when mitigation occurred.
This can reveal supplier-response problems during post-incident review.
For broader supplier governance, see Third-Party Risk Assessment Checklist.
Board and Executive Decisions
For major incidents, include governance milestones:
- board notified;
- emergency meeting;
- materiality determination;
- ransom-payment decision;
- public communication approved;
- business restoration approved.
These are often just as important as technical events.
Data Breach Timeline Metrics
A mature organization can derive useful metrics from the chronology.
| Metric | Calculation |
|---|---|
| Mean Time to Detect | compromise → detection |
| Mean Time to Escalate | detection → incident owner |
| Mean Time to Contain | detection → containment |
| Legal escalation time | confirmation → legal |
| Materiality decision time | review start → decision |
| Regulatory submission time | trigger → submission |
| Recovery time | incident → restored operations |
For detection metrics, see Mean Time to Detect.
Frequently Asked Questions
What is a data breach timeline template?
It is a structured chronology used to document technical events, decisions, containment actions, regulatory triggers, notifications, recovery and post-incident activity.
Should the timeline begin when the breach starts?
Record the earliest known attacker activity if available, but also record the separate time the organization first detected the event.
Those are often different.
Should a timeline include legal decisions?
Yes.
For regulated incidents, legal and compliance decision timestamps can be critical.
Does the SEC four-day clock start at detection?
No. For domestic registrants, the SEC Item 1.05 clock generally starts after the company determines the cybersecurity incident is material.
Does UK GDPR always require notification within 72 hours?
No.
The ICO requires notification of certain personal data breaches within 72 hours of awareness where feasible; not every breach requires notification.
Should non-reportable breaches still be recorded?
Yes. ICO guidance says organizations should maintain records of personal data breaches even if notification was not required.
Should the timeline be updated after regulator notification?
Yes.
Investigation, remediation, supplemental reporting and recovery may continue well after the first notice.
Should every event include an exact timestamp?
Use the most precise reliable time available.
If exact time is unknown, record that fact rather than inventing precision.
Which time zone should be used?
For multinational incident response, UTC is usually the easiest primary standard.
If local regulatory or operational times matter, record both.
Final Takeaway
A data breach timeline template is not merely an administrative form.
Used correctly, it becomes the backbone of the incident record.
A strong timeline answers:
What happened?
When did we know it?
What did we believe at that moment?
Who made the decision?
What action followed?
Which regulatory clock started?
When did we report?
When did we recover?
The most useful timeline does not attempt to make early information look perfect.
It preserves the evolution of the investigation honestly:
suspected → validated → confirmed → contained → assessed → reported → recovered → reviewed
NIST’s current guidance places incident response inside the broader cybersecurity risk-management lifecycle, reinforcing the value of disciplined detection, response, recovery and improvement processes.
For regulated organizations, the timeline has an additional role:
it proves not only what happened, but when the organization knew enough to act.
That distinction can be crucial when reporting deadlines are later reviewed.
Primary External Sources
Use these authoritative references at the bottom of the article:
NIST SP 800-61 Rev. 3 — Incident Response Recommendations
NIST finalized Revision 3 in April 2025 and says incident response should be integrated throughout cybersecurity risk-management activities.
ICO — Personal Data Breaches: A Guide
ICO guidance confirms the 72-hour rule for reportable personal-data breaches, notification of high-risk individuals, and recordkeeping even when regulator notification is unnecessary.
SEC — Cybersecurity Risk Management, Strategy, Governance and Incident Disclosure
The SEC explains that Item 1.05 filing is generally due within four business days after materiality determination, rather than discovery.