Dwell Time vs MTTD in Cybersecurity: Differences, Formulas and Measurement
Dwell time vs MTTD is one of the most commonly misunderstood comparisons in cybersecurity metrics.
Both measurements deal with the period before an attack is discovered, so they can appear almost identical.
But they serve different purposes.
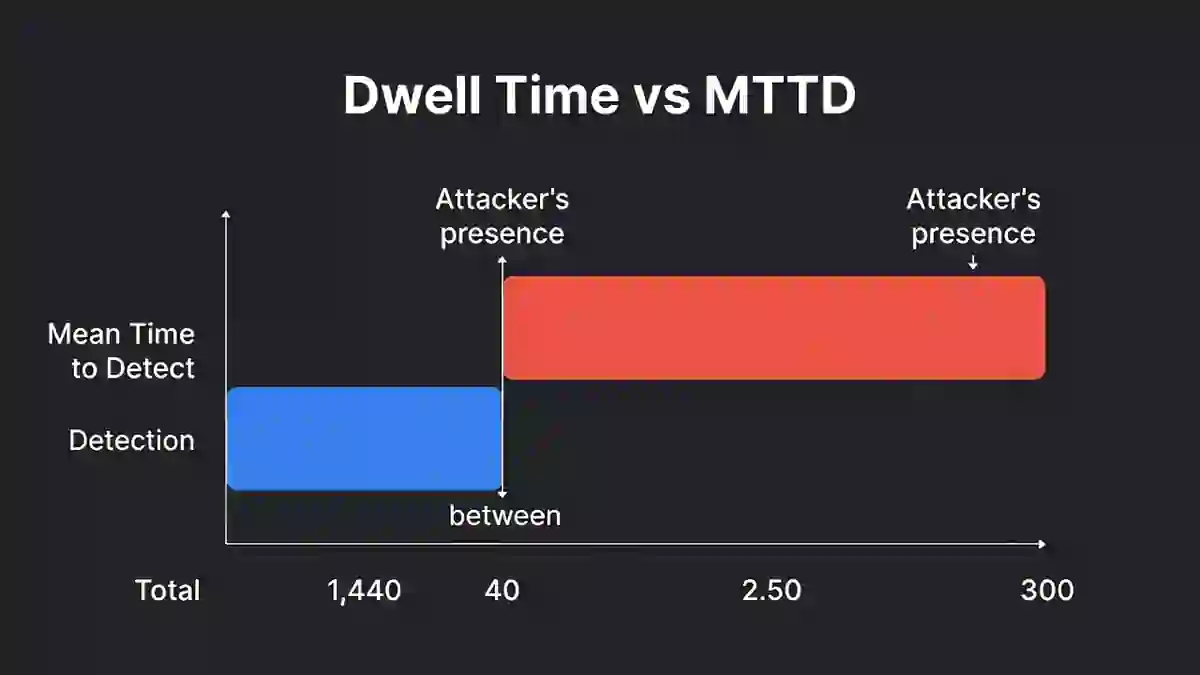
Dwell time generally describes how long an attacker remains present in an environment before the compromise is discovered or detected.
Mean Time to Detect (MTTD) is an organization-level performance metric calculated by averaging detection intervals across multiple incidents according to a defined measurement method.
That distinction matters because security teams sometimes take a published dwell-time statistic and treat it as if it were a universal MTTD benchmark.
It is not.
Mandiant’s M-Trends 2026, for example, reports a 14-day global median dwell time across its 2025 investigations. That figure describes the median dwell time in Mandiant’s investigation dataset; it does not mean every organization has an MTTD of 14 days.
The correct question is therefore not:
“Which metric is better?”
It is:
“What does each metric measure, and which operational problem are we trying to understand?”
Dwell Time vs MTTD at a Glance
| Area | Dwell Time | MTTD |
|---|---|---|
| Main purpose | Measure attacker exposure before discovery | Measure detection performance |
| Typical use | Individual incident or investigation dataset | Multiple incidents |
| Common statistic | Individual duration or median | Arithmetic mean |
| Start point | Initial compromise/activity | Defined incident start |
| End point | Discovery/detection | Detection |
| Useful for | Understanding hidden attacker presence | Measuring SOC detection trend |
| Main concern | How long attacker operated unnoticed | How efficiently organization detects |
| Common mistake | Treating investigation time as dwell time | Calculating “mean” from one incident |
The definitions may vary by organization or research methodology, so the start and end points should always be documented.
Table of Contents
What Is Dwell Time?
Dwell time generally refers to the period between an attacker gaining access to an environment and the compromise being discovered.
A simplified formula is:
Dwell Time = Discovery Time − Initial Compromise Time
Example:
Initial compromise: Monday 02:00
Discovery: Thursday 14:00
Dwell time:
3 days, 12 hours
That is the exposure period before discovery.
It does not normally include:
- containment;
- eradication;
- restoration;
- post-incident review.
Those happen after discovery and belong to other response metrics.
For a dedicated guide, see Dwell Time Cybersecurity.
What Mandiant Means by Dwell Time
Mandiant’s annual M-Trends reports are one of the most widely cited sources for attacker dwell-time research.
M-Trends 2026 reports:
Global median dwell time: 14 days
compared with:
11 days in the previous reporting period.
Mandiant says the increase was influenced in part by longer-running espionage and North Korean IT-worker activity. For those two categories, median dwell time was 122 days.
This shows why one overall number can hide very different attacker behaviors.
Some intrusions are discovered quickly.
Others remain hidden for months.
Dwell Time Is Usually a Median in Threat Research
Another important distinction is statistical.
Mandiant reports median dwell time, not mean dwell time.
Why?
Because dwell-time data can contain extreme outliers.
Imagine five incidents:
1 day
2 days
3 days
4 days
365 days
The mean becomes:
75 days
The median is:
3 days
The median better represents the middle case when one incident is extremely long.
This is one reason published dwell-time research should not be casually compared with internal MTTD.
What Is Mean Time to Detect (MTTD)?
Mean Time to Detect is an internal operational metric that measures average detection speed across a defined group of incidents.
A basic formula is:
MTTD = Total Detection Time ÷ Number of Incidents
Suppose three incidents have these detection intervals:
| Incident | Activity start | Detection | Interval |
|---|---|---|---|
| A | 08:00 | 08:15 | 15 min |
| B | 10:00 | 11:00 | 60 min |
| C | 14:00 | 14:30 | 30 min |
Total detection time:
15 + 60 + 30 = 105 minutes
Number of incidents:
3
Therefore:
MTTD = 105 ÷ 3 = 35 minutes
That is a true mean because it averages multiple incidents.
For the full calculation guide, see Mean Time to Detect (MTTD).
One Incident Does Not Have an MTTD
This is an important correction to the old article.
If an attacker enters at:
09:00
and detection occurs at:
15:00
you can say:
Detection interval = 6 hours
or:
That incident was detected after six hours.
You should not technically say:
“The MTTD was six hours.”
A mean requires a population of incidents.
This small terminology correction improves the credibility of the entire metrics cluster.
How MTTD Should Be Defined
The formula is simple.
The difficult part is determining the starting timestamp.
Possible definitions include:
- initial compromise;
- first confirmed malicious activity;
- first observable malicious event;
- first point the security controls could reasonably have detected.
The organization should choose a definition and apply it consistently.
For example:
MTTD starts at the first confirmed malicious event and ends when a security control or analyst identifies the incident.
That allows quarter-to-quarter comparison.
Difference 1: Dwell Time Measures Exposure; MTTD Measures Performance
The simplest distinction is:
Dwell time = attacker perspective
MTTD = defender performance perspective
Dwell time asks:
How long did the attacker remain undiscovered?
MTTD asks:
How quickly do we detect incidents on average?
They overlap in time but answer different questions.
Difference 2: Individual Incident vs Population Metric
Dwell time can be calculated for one intrusion.
Example:
Attacker remained undiscovered for 48 hours.
MTTD normally needs multiple incidents.
Example:
Average detection interval across 37 High/Critical incidents was 42 minutes.
This difference is fundamental.
Difference 3: Median vs Mean
External incident-response reports frequently publish a median dwell time.
MTTD contains the word:
Mean
and therefore usually refers to an arithmetic average.
You should not compare:
14-day median dwell time
with:
30-minute MTTD
as though one organization is dramatically outperforming “the global average.”
They are different statistics based on different populations and methodologies.
Difference 4: Dwell-Time Research Often Includes External Discovery
Mandiant reports not only how long attackers remain present but also how incidents were first discovered.
Across its 2025 investigations:
- 52% were first detected internally;
- 34% were disclosed by an external entity;
- 14% were revealed by adversaries.
This matters.
If law enforcement, a customer, a supplier, or an attacker tells the organization about the incident, the resulting dwell-time statistic still describes how long the compromise existed before discovery.
But that does not necessarily represent the SOC’s internal detection capability.
Internal Discovery vs External Discovery
A mature SOC should track this separately.
Example:
| Discovery source | Share |
|---|---|
| Internal SOC | 78% |
| Supplier | 8% |
| Customer | 5% |
| Researcher | 4% |
| Law enforcement | 3% |
| Attacker | 2% |
These values are illustrative.
A rising percentage of external discovery may indicate:
- visibility gaps;
- weak monitoring;
- poor third-party integration.
For broader operational metrics, see SOC Efficiency Metrics 2026.
Difference 5: MTTD Helps Measure Detection Engineering
MTTD can help evaluate improvements in:
- SIEM rules;
- EDR detections;
- identity monitoring;
- cloud telemetry;
- network detection;
- alert correlation.
Suppose:
Q1 MTTD = 70 minutes
Q2 MTTD = 48 minutes
Q3 MTTD = 31 minutes
If the measurement methodology remained consistent, that trend suggests detection performance is improving.
Difference 6: Dwell Time Shows the Hidden Exposure Window
Dwell time is particularly useful in post-incident analysis.
Imagine:
Compromise: January 1
First attacker persistence: January 2
Credential theft: January 10
Data exfiltration: February 5
Discovery: March 1
The organization may have detected the final suspicious activity quickly.
But the attacker was already present for nearly two months.
That historical exposure matters.
Difference 7: Dwell Time and MTTD Can Move Differently
It is possible for internal MTTD to improve while certain major incidents continue to have long dwell times.
Example:
Most malware incidents:
detected in 15 minutes
One sophisticated edge-device compromise:
undetected for 180 days
The organization’s mean detection performance may still look good if the incident population is dominated by easy-to-detect malware.
The long dwell-time incident reveals a different risk:
visibility blind spots.
That is why both metrics are useful.
Dwell Time and Edge-Device Blind Spots
Mandiant’s M-Trends 2026 specifically highlights attackers maintaining persistence in infrastructure that often lacks standard telemetry, including edge devices.
This is especially important because many organizations have excellent endpoint monitoring but weaker visibility into:
- VPN appliances;
- firewalls;
- network infrastructure;
- virtualization;
- management systems.
A low endpoint MTTD does not guarantee low enterprise dwell time.
Dwell Time vs MTTD Timeline Example
Consider this hypothetical intrusion.
Day 0, 01:00 — VPN vulnerability exploited.
Day 0, 01:15 — attacker gains credentials.
Day 1 — attacker creates persistence.
Day 3 — lateral movement begins.
Day 5, 08:00 — unusual authentication activity appears.
Day 5, 08:05 — SIEM generates alert.
Day 5, 08:12 — analyst acknowledges.
Day 5, 08:30 — incident confirmed.
Possible measurements:
Dwell time: approximately five days to discovery.
Detection latency from observable event: 5 minutes.
Analyst acknowledgement time: 7 minutes.
Validation time: 18 minutes.
This incident shows why:
one security event can produce several legitimate time measurements.
Dwell Time vs MTTD vs MTTA vs MTTC
A cleaner incident-response model is:
| Metric | Example interval |
|---|---|
| Dwell Time | Initial compromise → discovery |
| MTTD | Defined incident start → detection, averaged across incidents |
| MTTA | Alert generated → analyst acknowledgement |
| Validation Time | Acknowledgement → incident confirmation |
| MTTC | Incident confirmation → effective containment |
| Recovery Time | Containment/remediation → trusted operation restored |
For the complete comparison, see MTTD vs MTTR vs MTTC vs Dwell Time.
Dwell Time Does Not Include Containment by Default
Your old article effectively treats investigation, confirmation, and containment delay as part of dwell time.
I recommend removing that.
Once the incident is discovered, subsequent time should be represented separately using metrics such as:
- acknowledgement time;
- investigation/validation time;
- MTTC;
- recovery time.
This gives readers a much clearer model.
Why Dwell Time Matters in 2026
M-Trends 2026 demonstrates that stealthy intrusions remain a serious problem.
Global median dwell time rose to 14 days, and certain espionage/IT-worker cases had much longer median presence.
But the same research also shows another reality:
some attackers move extremely quickly after access.
Mandiant reports that some initial-access hand-offs can occur in less than 30 seconds.
Security programs therefore need to address both:
long-term stealth
and:
rapid escalation.
Why MTTD Matters in 2026
MTTD helps security teams evaluate their own detection capability.
Use it to answer:
- Are Critical incidents detected faster?
- Are cloud incidents slower than endpoint incidents?
- Are identity attacks taking too long?
- Which detections depend on users reporting problems?
- Are detection improvements working?
For the broader statistics discussion, see Average Cyber Attack Detection Time in 2026.
Measure MTTD by Severity
A single enterprise-wide MTTD can hide meaningful variation.
Example:
| Severity | MTTD |
|---|---|
| Critical | 9 min |
| High | 19 min |
| Medium | 48 min |
| Low | 3.4 hrs |
These values are illustrative.
The purpose is to make sure the most dangerous events receive the fastest detection.
Measure MTTD by Detection Source
Another useful breakdown:
| Detection source | MTTD |
|---|---|
| EDR | 12 min |
| Identity | 18 min |
| SIEM | 31 min |
| Cloud | 47 min |
| Network | 26 min |
| User report | 3 hrs |
| Supplier | 9 hrs |
Again, illustrative.
This shows where visibility gaps exist.
Mean, Median and Percentiles
Do not report only one statistic.
For internal detection performance, consider:
Mean
Useful for overall average.
Median
Shows the middle incident.
P90/P95
Shows long-tail detection failures.
Example:
Mean MTTD: 33 min
Median: 18 min
P90: 2.8 hrs
P95: 9 hrs
That tells a much more complete story.
Dwell Time and SOC Performance Are Related, Not Identical
A long dwell time can indicate:
- poor telemetry;
- undetected edge devices;
- stealthy attacker behavior;
- identity blind spots.
But it does not automatically mean:
“SOC analysts were slow.”
The attacker may have operated in infrastructure outside the SOC’s monitoring scope.
The root cause matters.
Which Metric Should Security Teams Prioritize?
Do not choose one.
Use both for different purposes.
Prioritize MTTD when you want to improve:
- alerting;
- monitoring;
- detection engineering;
- SOC performance.
Prioritize dwell time when you want to understand:
- historical attacker presence;
- blind spots;
- stealth;
- exposure duration.
Together they answer:
How long did the attacker remain hidden?
and:
How well are we detecting incidents operationally?
Dwell Time and Containment Are Separate Problems
Suppose:
Dwell time = 40 days
but after discovery:
MTTC = 12 minutes
The organization detected the attack very late but contained it quickly.
Now reverse it:
Dwell time = 10 minutes
MTTC = 5 hours
The threat was found quickly but not controlled.
These scenarios require different improvements.
For containment, see Mean Time to Contain.
Regulatory Reporting: Do Not Use Dwell Time or MTTD as Legal Clocks
This is another important correction to the current page.
Your existing article says detection timing influences:
- CIRCIA reporting;
- SEC disclosure;
- UK 72-hour reporting.
That is directionally true for readiness, but the legal clocks are not simply MTTD or dwell time.
SEC
For domestic public-company registrants, Item 1.05 Form 8-K is generally due within four business days after the company determines a cybersecurity incident is material.
The SEC explicitly says the deadline is tied to materiality determination, not discovery, and materiality must be assessed without unreasonable delay.
So:
MTTD ≠ SEC reporting clock
UK GDPR
UK GDPR reporting applies to certain personal data breaches.
The ICO states that a notifiable breach must generally be reported without undue delay and no later than 72 hours after the organization becomes aware of it.
So:
dwell time ≠ UK GDPR 72-hour clock
and:
MTTD ≠ automatically the awareness timestamp.
CIRCIA
CIRCIA’s statutory framework includes future 72-hour covered-incident reporting and 24-hour ransom-payment reporting once the mandatory final rule takes effect.
Do not describe the 72-hour CIRCIA clock as a universal current operational deadline until the applicable final rule is effective.
Use the phrase:
CIRCIA reporting readiness
where appropriate.
Operational Timeline vs Legal Timeline
A mature incident record should track both.
Example:
| Event | Timestamp |
|---|---|
| Initial compromise | Day 0 |
| First detection | Day 3 |
| Incident confirmed | Day 3 |
| Personal-data breach awareness | Day 3 |
| Materiality review begins | Day 4 |
| Materiality determined | Day 4 |
| Effective containment | Day 4 |
From this one incident you can derive:
- dwell time;
- detection interval;
- validation time;
- containment time;
- legal trigger timestamps.
For a reusable chronology, see Data Breach Timeline Template.
Common Dwell Time vs MTTD Mistakes
1. Calling One Incident’s Detection Time “MTTD”
MTTD requires averaging multiple incidents.
2. Treating Dwell Time as the Entire Incident Lifecycle
Dwell time generally ends at discovery/detection.
Containment and recovery are separate.
3. Comparing Mean MTTD With Median Dwell Time Directly
They are different statistical measures.
4. Treating Mandiant’s 14 Days as a Universal MTTD Benchmark
It is a median dwell-time statistic from Mandiant’s investigation dataset.
5. Ignoring External Discovery
An attacker discovered by law enforcement is different from one detected internally by your SOC.
6. Using Different MTTD Start Points
Define your metric consistently.
7. Reporting Only the Mean
Use median and percentiles too.
8. Assuming Fast Endpoint Detection Means Low Enterprise Dwell Time
Edge devices, identity systems, cloud and virtualization may still have blind spots.
9. Treating Regulatory Clocks as Security Metrics
Legal reporting triggers must be assessed separately.
Cybersecurity Time Detection Measurement Framework
I recommend this model:
Initial compromise
↓
Attacker undiscovered
← Dwell Time →
↓
Detection
← MTTD ends →
↓
Acknowledgement
↓
Validation
↓
Response
↓
Effective containment
↓
Eradication
↓
Recovery
This is much clearer than the current graphic.
Example Quarterly Detection Dashboard
| Metric | Q1 | Q2 | Q3 |
|---|---|---|---|
| Mean MTTD | 51 min | 39 min | 30 min |
| Median MTTD | 28 min | 22 min | 17 min |
| P90 MTTD | 4.0 hrs | 3.0 hrs | 2.1 hrs |
| Internal discovery | 72% | 78% | 82% |
| Longest confirmed dwell time | 21 days | 9 days | 4 days |
| Critical MTTD | 16 min | 12 min | 8 min |
These are illustrative values, not industry standards.
Questions CISOs Should Ask
Instead of asking only:
“What is our MTTD?”
ask:
- Which attacks have the longest dwell time?
- Which systems are invisible to our SOC?
- What is our P95 detection time?
- How many serious incidents are discovered externally?
- Are Critical incidents detected faster?
- Are cloud and identity attacks slower to detect?
- Is our telemetry sufficient on edge devices?
Those questions provide much stronger insight.
Frequently Asked Questions
What is dwell time in cybersecurity?
Dwell time generally refers to the period between initial attacker compromise or activity and discovery of the intrusion.
What is MTTD?
Mean Time to Detect is the average detection interval across a defined set of incidents.
Is MTTD the same as dwell time?
No.
They overlap conceptually, but dwell time usually describes attacker exposure in an incident or investigation dataset, while MTTD is generally an internal mean detection metric.
Can one incident have an MTTD?
Strictly speaking, no.
One incident has a detection interval.
MTTD is the average across multiple incidents.
Does dwell time include containment?
Normally no.
Containment should be measured separately.
What is the current global dwell-time statistic?
Mandiant’s M-Trends 2026 reports a 14-day global median dwell time across its 2025 investigations.
That is not a universal global MTTD.
Why did Mandiant’s dwell time increase?
Mandiant says the shift was influenced by stealthier activity, including espionage and North Korean IT-worker cases; both categories showed a 122-day median dwell time in its dataset.
What percentage of incidents are detected internally?
Mandiant reports that organizations first detected evidence of malicious activity internally in 52% of its 2025 investigations, up from 43% the previous year.
That is dataset-specific, not a universal benchmark.
Does the SEC four-day clock start at detection?
No.
The SEC says Item 1.05 is generally due four business days after the company determines the incident is material, not four days after detection.
Does UK GDPR reporting start at MTTD?
Not necessarily.
The ICO’s 72-hour period is tied to awareness of a reportable personal data breach.
Final Takeaway
Dwell time and MTTD measure related but different things.
A useful distinction is:
Dwell time
How long did the attacker remain undiscovered?
MTTD
How quickly does our organization detect incidents on average?
Dwell time is particularly useful for:
- retrospective exposure analysis;
- understanding stealth;
- identifying visibility gaps.
MTTD is particularly useful for:
- SOC performance;
- detection engineering;
- operational trend analysis.
The two should not be collapsed into one number.
Current Mandiant data illustrates the importance of this distinction. Its M-Trends 2026 research reports a 14-day global median dwell time, 52% internal discovery, and much longer dwell times for some stealth-focused threat categories.
At the same time, NIST’s current incident-response guidance emphasizes improving the effectiveness of detection, response and recovery together, rather than optimizing one isolated metric.
The strongest security question is therefore not:
“Is dwell time or MTTD more important?”
It is:
“Where are attackers remaining invisible, how quickly are we detecting incidents we can see, and which blind spots are creating the longest exposure?”
That is the operational insight these metrics should provide.
Recommended Links
Mean Time to Detect (MTTD)
Mean Time to Detect (MTTD)
Dwell Time Cybersecurity
Dwell Time Cybersecurity
MTTD vs MTTR vs MTTC vs Dwell Time
MTTD vs MTTR vs MTTC vs Dwell Time
Average Cyber Attack Detection Time
Average Cyber Attack Detection Time 2026
SOC Efficiency Metrics 2026
SOC Efficiency Metrics 2026
Cybersecurity Incident Response Timeline
Cybersecurity Incident Response Timeline
Data Breach Timeline Template
Data Breach Timeline Template