Cyber Incident Reporting Deadlines 2026: US vs UK Rules Compared
Cyber incident reporting is no longer governed by one universal deadline.
In both the United States and the United Kingdom, a single security incident may trigger several different legal or regulatory clocks depending on:
- what kind of organization experienced the incident;
- whether personal data was affected;
- whether the incident is material to investors;
- whether the organization operates critical infrastructure;
- whether a ransom payment was made;
- whether sector-specific rules apply.
That means a statement such as:
“Cyber incidents must be reported within 72 hours”
or:
“US companies have four business days”
is usually too broad.
The correct question is:
Which reporting regime applies, what event starts its clock, and who receives the report?
For example:
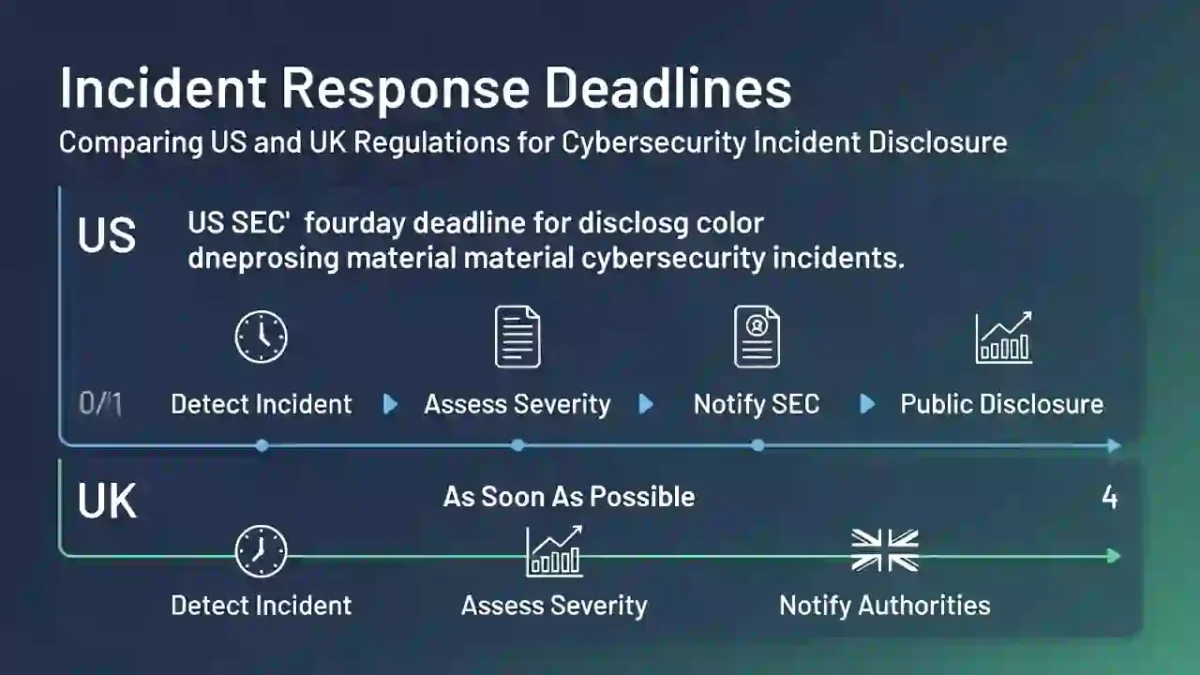
- an SEC registrant may have a four-business-day Form 8-K deadline after materiality determination;
- a UK controller may have 72 hours after becoming aware of a reportable personal data breach to notify the ICO;
- the proposed UK Cyber Security and Resilience Bill uses a separate 24-hour initial and 72-hour fuller reporting structure for regulated entities;
- CIRCIA’s proposed U.S. framework uses 72 hours for covered cyber incidents and 24 hours for ransom payments, although mandatory CIRCIA reporting is not yet effective.
This guide compares the principal U.S. and UK reporting clocks that security, legal, compliance and executive teams should understand in 2026.
Cyber Incident Reporting Deadlines at a Glance
| Regime | Who may be affected | Trigger | Main deadline | Current status |
|---|---|---|---|---|
| SEC Item 1.05 | U.S. public-company registrants | Materiality determination | 4 business days | In force |
| CIRCIA | Covered critical-infrastructure entities | Reasonable belief covered cyber incident occurred | Proposed 72 hours | Final mandatory rule not yet effective |
| CIRCIA ransom-payment reporting | Covered entities | Ransom payment disbursed | Proposed 24 hours | Not yet effective |
| UK GDPR | Controllers with reportable personal data breach | Awareness of reportable breach | 72 hours | In force |
| UK PECR | Relevant public electronic communications providers | Awareness of breach | 72 hours | In force |
| UK Cyber Security and Resilience Bill | Proposed regulated entities | Awareness of reportable incident | Proposed 24h initial + 72h fuller report | Bill, not yet law |
This table is a high-level comparison. A real incident may involve several regimes simultaneously.
Table of Contents
Why US vs UK Cyber Reporting Is More Complicated Than It Looks
The main difficulty is not remembering the numbers.
It is understanding the trigger.
Four different regulations might use four different concepts:
- materiality determination;
- awareness;
- reasonable belief;
- reportable incident classification.
Those are not interchangeable.
Consider one ransomware attack.
The security team may detect suspicious activity on Monday.
Later Monday, personal data exposure becomes reasonably certain.
On Tuesday, executives determine the event is material to investors.
On Wednesday, the company pays a ransom.
That single incident may produce multiple separate clocks.
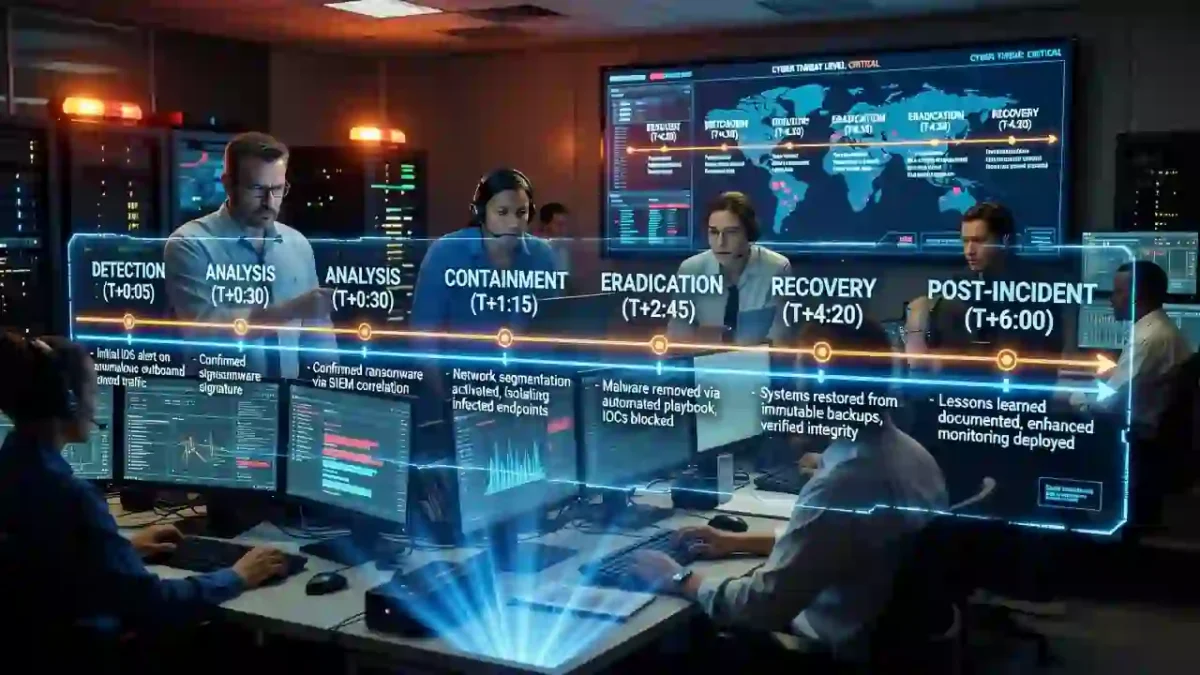
A strong incident-response program should therefore record decision timestamps, not merely the date the attack occurred.
1. SEC Cybersecurity Disclosure: Four Business Days
For U.S. public companies, one of the most important rules is SEC Form 8-K Item 1.05.
A domestic registrant must generally disclose a cybersecurity incident it determines is material within four business days after the materiality determination.
The SEC makes an important distinction:
The filing deadline is not tied to discovery.
It is tied to the company’s determination that the incident is material.
SEC Timeline Example
Monday, 08:00
Security detects suspicious activity.
Monday, 15:00
Unauthorized access is confirmed.
Tuesday, 11:00
The company evaluates operational and financial effects.
Tuesday, 16:00
The company determines the incident is material.
The SEC four-business-day clock begins from that materiality determination, subject to applicable filing rules.
For a full SEC workflow, see SEC Cyber Incident Disclosure Checklist.
And for the timing mechanics, see SEC Cyber Rule Timeline 2026.
What Does “Material” Mean for the SEC?
The SEC uses the traditional securities-law materiality standard.
An incident is material when there is a substantial likelihood that a reasonable shareholder would consider the information important in making an investment decision, or when the information would significantly alter the total mix of information available.
Factors may include:
- financial impact;
- operational disruption;
- customer effects;
- strategic data theft;
- regulatory consequences;
- litigation;
- reputational effects;
- reasonably likely future impact.
There is no simple SEC rule such as:
“More than $5 million = material.”
Materiality is context-specific.
SEC Materiality Must Be Determined Without Unreasonable Delay
A company cannot deliberately postpone the materiality decision simply to avoid starting the four-business-day clock.
The SEC instructs registrants to make the determination without unreasonable delay.
That makes internal escalation important.
Security, legal, finance and executive teams should not operate serially:
security investigates for three days → then legal is called → then finance starts impact review
A better model is parallel escalation.
SEC Item 1.05 vs Item 8.01
Another distinction matters.
The SEC clarified that Item 1.05 is intended for incidents determined to be material.
If a company voluntarily discloses:
- an incident it has determined is immaterial; or
- an incident whose materiality has not yet been determined,
SEC staff encourages the use of another Form 8-K item, such as Item 8.01.
A voluntary disclosure does not eliminate the continuing obligation to determine materiality.
2. UK GDPR: 72 Hours for Certain Personal Data Breaches
The UK GDPR rule is fundamentally different.
The ICO says organizations must notify it of certain personal data breaches without undue delay and, where feasible, within 72 hours after becoming aware of the breach.
But an important qualification is often omitted:
Not every personal data breach must be reported to the ICO.
The notification obligation applies where the breach is likely to result in a risk to individuals’ rights and freedoms.
This makes your current article’s blanket phrase “UK organizations must notify the ICO within 72 hours” too broad.
What Counts as a Personal Data Breach?
A personal data breach can involve more than stolen data.
It may involve a security breach leading to:
- accidental destruction;
- unlawful destruction;
- loss;
- alteration;
- unauthorized disclosure;
- unauthorized access
to personal data.
A ransomware incident can therefore become a UK GDPR breach if personal information is:
- accessed;
- exfiltrated;
- encrypted and made unavailable;
- altered;
- lost.
But a cyber incident involving no personal data may not trigger the UK GDPR breach-notification rule at all.
When Does the UK GDPR Clock Start?
The ICO says the reporting period begins when the organization becomes aware of the personal data breach.
The ICO’s self-assessment guidance explains awareness as the point where the controller has a reasonable degree of certainty that a personal data breach has occurred.
That is different from:
- first network alert;
- attacker entry time;
- full forensic confirmation.
UK GDPR Timeline Example
Monday, 08:00
EDR detects suspicious activity.
No confirmed personal-data breach yet.
Monday, 14:00
Investigation finds evidence that a database containing personal information was accessed.
Monday, 17:00
The organization has a reasonable degree of certainty that a personal data breach occurred.
The 72-hour awareness period now becomes relevant if the breach meets the reporting threshold.
What Must Be Reported to the ICO?
The ICO says the notification should include, where possible:
- the nature of the personal data breach;
- categories and approximate number of people affected;
- categories and approximate number of records affected;
- DPO or other contact details;
- likely consequences;
- measures taken or proposed to address the breach.
Organizations do not have to wait until every fact is known.
The ICO explicitly promotes a report early, update later approach where the 72-hour deadline arrives before the full investigation is complete.
High-Risk Breaches Also Require Individual Notification
The ICO reporting obligation is not always the end of the process.
If the breach is likely to result in a high risk to affected individuals’ rights and freedoms, those individuals must generally also be informed without undue delay.
That creates two different communication paths:
risk → ICO notification
high risk → affected individuals also notified
All Personal Data Breaches Should Be Recorded
Even where a breach is not reportable to the ICO, the organization should document it.
ICO guidance says organizations should keep records of personal data breaches regardless of whether notification was required.
A good breach record includes:
- facts;
- effects;
- remedial action;
- reasoning for notification or non-notification.
3. UK PECR: Now Also 72 Hours
There is another UK reporting rule worth adding because it changed recently.
The Data (Use and Access) Act 2025 changed PECR’s breach-reporting period for relevant providers from the previous 24-hour model to 72 hours after awareness.
The ICO updated its guidance in August 2025 to reflect this change.
This means some organizations may face:
- UK GDPR reporting;
- PECR reporting;
- other sector obligations
from the same security incident.
4. UK Cyber Security and Resilience Bill: Proposed 24/72-Hour Reporting
The UK is also developing a broader cyber incident-reporting regime through the Cyber Security and Resilience Bill.
The government says the Bill would introduce:
Initial notification
Within 24 hours of becoming aware that a reportable incident is taking place.
Fuller notification
Within 72 hours.
The notification would go to the relevant regulator, with the NCSC receiving the same information.
This is separate from the UK GDPR.
It targets cyber resilience and regulated services, rather than personal-data protection.
UK Cyber Bill vs UK GDPR
| Topic | UK GDPR | Cyber Security and Resilience Bill |
|---|---|---|
| Main concern | Personal-data protection | Cyber resilience / regulated services |
| Trigger | Awareness of reportable personal data breach | Awareness of qualifying regulated incident |
| Initial deadline | 72 hours | Proposed 24 hours |
| Fuller report | Updates as needed | Proposed 72 hours |
| Main recipient | ICO | Relevant regulator + NCSC |
| Current status | In force | Proposed Bill |
One event could potentially trigger both.
For the full proposed UK regime, see UK Cyber Security and Resilience Bill 2026.
5. CIRCIA: Proposed 72-Hour U.S. Critical-Infrastructure Reporting
The U.S. comparison should not stop with the SEC.
CIRCIA creates a separate federal reporting framework for certain critical-infrastructure entities.
The proposed framework uses:
- 72 hours for a covered cyber incident;
- 24 hours for a ransom payment.
However, mandatory CIRCIA reporting is not yet effective until the final rule takes effect.
For the current status and readiness workflow, see CIRCIA 2026.
This distinction is essential because:
SEC = investor/materiality disclosure
while:
CIRCIA = critical-infrastructure government reporting
A company could theoretically be subject to both.
US vs UK Reporting Trigger Comparison
The most useful comparison is not by country alone.
It is by trigger.
| Regime | Trigger |
|---|---|
| SEC Item 1.05 | Company determines incident is material |
| CIRCIA proposed | Entity reasonably believes covered cyber incident occurred |
| CIRCIA ransom report | Ransom payment is disbursed |
| UK GDPR | Controller becomes aware of reportable personal-data breach |
| UK PECR | Relevant provider becomes aware of qualifying breach |
| UK Cyber Bill proposed | Entity becomes aware of qualifying incident |
This is why one universal “incident start time” is not enough.
Cybersecurity Time Regulatory Clock Record
During a serious incident, record each timestamp separately.
| Timestamp | Example |
|---|---|
| Attack likely began | 02:10 |
| SOC first detected | 06:45 |
| Incident confirmed | 10:20 |
| Personal data breach awareness | 13:30 |
| CIRCIA classification / reasonable belief | 14:10 |
| SEC materiality review started | 15:00 |
| SEC materiality determined | Next day, 09:15 |
| Ransom paid | Next day, 17:40 |
One incident may create multiple clocks.
This is far more useful than recording simply:
Incident date: Monday.
6. One Incident Can Trigger Several Regulators
Consider a hypothetical multinational public company operating critical services in both the United States and United Kingdom.
A ransomware attacker:
- disrupts operations;
- steals customer personal data;
- compromises a critical U.S. service;
- causes a material financial effect;
- receives a ransom payment.
The company may need to consider:
SEC
Was the incident material?
If yes:
Item 1.05 → four business days from materiality determination.
UK GDPR
Was there a reportable personal-data breach?
If yes:
ICO → within 72 hours of awareness.
CIRCIA
If the company is a covered entity and the final rule is in effect:
covered cyber incident → 72 hours.
CIRCIA ransom payment
If applicable:
payment → 24 hours.
UK cyber resilience regime
If the Bill later becomes law and the entity/service is in scope:
24-hour initial + 72-hour fuller report.
One incident therefore needs:
one investigation → multiple legal analyses → multiple reporting outputs.
Cybersecurity Time Multi-Regulator Decision Matrix
| Question | SEC | UK GDPR | CIRCIA | UK Cyber Bill |
|---|---|---|---|---|
| Does personal data matter? | Possibly | Central | Not necessarily | Not necessarily |
| Is investor materiality required? | Yes | No | No | No |
| Critical-infrastructure status relevant? | No | No | Yes | Regulated-service scope |
| Main clock | 4 business days | 72 hours | Proposed 72h | Proposed 24h/72h |
| Public disclosure? | Yes | Generally regulator/individuals | Government report | Regulator/NCSC |
| Current law? | Yes | Yes | Mandatory final rule not yet effective | Bill |
Detection Speed Still Matters — But Not Because Every Clock Starts at Detection
Your current article says detection speed affects compliance, which is correct, but it should explain why.
Detection does not automatically start:
- the SEC materiality clock;
- the UK GDPR awareness clock in every case;
- every other regulatory clock.
But poor detection makes every later step harder.
Long dwell time can increase:
- operational impact;
- data loss;
- financial loss;
- customer harm;
- likelihood that an event becomes material;
- number of regulators involved.
For more detail, see Dwell Time Cybersecurity and Mean Time to Detect.
Do Not Confuse MTTD With Regulatory Awareness
This distinction is important.
MTTD
An operational cybersecurity metric.
It measures how quickly a security team detects malicious activity.
Regulatory awareness
A legal concept that depends on the applicable rule.
For UK GDPR, awareness generally involves a reasonable degree of certainty that a personal data breach occurred.
Materiality determination
An SEC securities-law decision.
These three events may occur hours or days apart.
7. Third-Party Notification Speed Can Determine Compliance Success
Modern organizations depend on:
- cloud providers;
- MSPs;
- SaaS suppliers;
- payment processors;
- hosting providers;
- security vendors.
Sometimes the vendor discovers the incident first.
If a supplier does not notify the customer promptly, the customer may be unable to:
- determine awareness;
- assess materiality;
- identify personal-data exposure;
- meet regulatory deadlines.
Supplier contracts should therefore include meaningful cyber-notification timelines.
For supplier governance, use the Third-Party Risk Assessment Checklist and Supplier Cybersecurity Contract Template.
Processor vs Controller Under UK GDPR
The UK GDPR creates an especially important supplier distinction.
A processor that becomes aware of a personal data breach must notify the controller without undue delay.
The controller is generally responsible for determining whether regulatory notification to the ICO is required.
This means contracts between controllers and processors should define:
- notification time;
- 24/7 contact;
- initial information requirements;
- evidence;
- update obligations.
The ICO specifically advises that breach-reporting requirements should be addressed in controller/processor contracts.
8. What Should a Regulatory Incident Record Contain?
Create one central incident record that can support multiple filings.
Include:
Timeline
- detection;
- confirmation;
- awareness;
- classification;
- materiality determination;
- reporting times.
Technical information
- affected systems;
- attacker activity;
- containment;
- indicators.
Data impact
- data categories;
- number of individuals;
- records affected.
Business impact
- outage;
- revenue effect;
- critical services;
- customer harm.
Regulatory decisions
- UK GDPR reportable? Why?
- SEC material? Why?
- CIRCIA applicable?
- sector reporting required?
Communications
- regulator reports;
- customer notices;
- investor disclosure;
- law-enforcement contact.
For a ready-made chronology framework, see Data Breach Timeline Template.
US vs UK Incident Reporting RACI
| Activity | Primary owner | Supporting teams |
|---|---|---|
| Detect attack | SOC | IT |
| Technical investigation | Incident Response | Vendor/Forensics |
| Personal-data breach assessment | Privacy/DPO | Legal, Security |
| SEC materiality assessment | Legal/Finance | Security, Executive |
| Critical-infrastructure analysis | Regulatory/Legal | Operations |
| ICO submission | Privacy/DPO | Legal |
| SEC Form 8-K | SEC Reporting/Legal | IR, Finance |
| CISA reporting | Regulatory owner | Security |
| Customer communication | Communications/Legal | Business |
| Board escalation | Executive/Corporate Secretary | CISO |
This is an example operating model rather than a regulatory requirement.
First 24 Hours of a Cross-Border Cyber Incident
Hour 0–1
- activate incident response;
- preserve evidence;
- assign incident commander;
- record detection time.
Hours 1–4
Determine:
- affected entities;
- affected systems;
- jurisdictions;
- personal-data involvement;
- critical-service involvement.
Hours 4–8
Notify:
- General Counsel;
- privacy/DPO;
- SEC reporting team where relevant;
- regulatory affairs;
- executives.
Hours 8–12
Begin parallel analyses:
- UK GDPR risk;
- SEC materiality;
- CIRCIA coverage;
- contractual reporting;
- sector requirements.
Hours 12–24
Document:
- current facts;
- unknowns;
- reporting triggers;
- exact regulatory timestamps;
- required notifications.
The objective is not to file everything in 24 hours.
The objective is to know which clocks are actually running.
Cybersecurity Time Cross-Border Reporting Checklist
Jurisdiction
- Which legal entities are affected?
- US?
- UK?
- EU?
- Other states/countries?
Data
- Personal data involved?
- What categories?
- How many people?
Business
- Critical service disrupted?
- Financial impact?
- Customers affected?
SEC
- Public registrant?
- Materiality review started?
- Materiality determined?
UK GDPR
- Personal data breach?
- Risk to rights and freedoms?
- Awareness timestamp recorded?
Critical Infrastructure
- CIRCIA likely applicable?
- UK regulated-service regime applicable?
Third Parties
- Vendor involved?
- When did vendor become aware?
- Contractual reporting requirements?
Documentation
- One central chronology?
- Decisions recorded?
- Reporting receipts retained?
Common US vs UK Reporting Mistakes
Mistake 1: Saying “All UK Cyber Incidents Must Be Reported Within 72 Hours”
False.
UK GDPR requires notification of certain reportable personal data breaches, not every cyber incident.
Mistake 2: Saying “The US Has a Four-Day Cyber Reporting Rule”
Too broad.
The SEC four-business-day rule applies to material cyber incidents for covered registrants and is tied to the materiality determination.
Other U.S. rules use different clocks.
Mistake 3: Starting Every Clock at Detection
Different regulations define different triggers.
Mistake 4: Waiting for Complete Investigation
ICO guidance explicitly allows organizations to report what they know and provide further information later.
The SEC similarly permits later amendments where required information was unavailable at the initial Item 1.05 filing.
Mistake 5: Treating Regulatory Reports as Interchangeable
An SEC disclosure is designed for investors.
An ICO notification is a data-protection notification.
A CISA report serves government cyber visibility.
They should be coordinated but not copied blindly.
Mistake 6: Ignoring Supplier Awareness
Third-party incidents can create reporting obligations for the customer organization.
Mistake 7: Maintaining Separate Conflicting Timelines
Use one authoritative incident chronology.
Worked Cross-Border Example
Imagine a U.S.-listed company with UK customers.
Monday, 07:00
Security detects ransomware.
Monday, 10:00
Investigation confirms attackers accessed UK customer information.
Monday, 14:00
The organization reaches a reasonable degree of certainty that a personal data breach occurred.
UK GDPR awareness analysis begins.
Tuesday, 09:00
Finance estimates material disruption to revenue.
Tuesday, 15:00
Management determines the incident is material.
The SEC four-business-day clock begins.
Wednesday
New forensic evidence changes the number of UK individuals affected.
The ICO can receive further information after the initial report if necessary.
This example shows why:
one attack does not mean one regulatory clock.
How the UK NIS Framework Can Also Interact With GDPR
The ICO specifically notes that an organization subject to UK NIS may need to report an incident to its competent authority and separately notify the ICO where the same event causes a personal data breach.
That provides a useful real-world example of parallel UK reporting.
A security event can be:
- a NIS incident;
- a UK GDPR personal data breach;
- both;
- neither.
Classification matters.
Executive Strategy for 2026
1. Build a Regulatory Trigger Matrix
For each rule, record:
- scope;
- trigger;
- deadline;
- regulator;
- reporting owner.
2. Integrate Legal Into Incident Response Early
Do not wait until the SOC finishes containment.
3. Record Decision Times
Especially:
- UK GDPR awareness;
- SEC materiality determination;
- ransom payment;
- critical-infrastructure classification.
4. Shorten Supplier Notifications
Your supplier notification deadline should be comfortably shorter than the tightest regulatory deadline you may face.
5. Conduct Cross-Border Tabletop Exercises
Test:
- SEC;
- UK GDPR;
- sector reporting;
- CIRCIA;
- contractual duties
in one scenario.
6. Measure Detection and Escalation
Track:
- MTTD;
- time to legal escalation;
- time to privacy escalation;
- time to materiality review;
- time to regulatory submission.
7. Give the Board a Regulatory Clock Dashboard
A useful dashboard can show:
| Metric | Target |
|---|---|
| Incident → legal escalation | Defined SLA |
| Personal breach → privacy review | Defined SLA |
| Major incident → executive escalation | Defined SLA |
| Materiality decision documentation | 100% |
| Regulatory deadline missed | 0 |
| Vendor late notification events | Trending downward |
Frequently Asked Questions
Do U.S. companies have to report every cyber incident within four days?
No.
SEC Item 1.05 generally applies after a registrant determines a cybersecurity incident is material.
Does the SEC clock start when the attack is discovered?
No.
It is generally tied to the materiality determination, which must be made without unreasonable delay.
Must every UK cyber incident be reported to the ICO within 72 hours?
No.
The UK GDPR requirement applies to reportable personal data breaches that are likely to result in a risk to individuals’ rights and freedoms.
When does the UK GDPR 72-hour period start?
When the organization becomes aware of the personal data breach. The ICO describes awareness as having a reasonable degree of certainty that the breach occurred.
What if all information is not available within 72 hours?
The ICO says organizations should report within the required timeframe using available information and provide additional information later without undue delay.
Must affected individuals also be informed?
If the breach is likely to result in a high risk to individuals’ rights and freedoms, affected individuals generally must be informed without undue delay.
What reporting deadlines does the proposed UK Cyber Security and Resilience Bill use?
The government proposes an initial notification within 24 hours of awareness, followed by a fuller report within 72 hours for regulated incidents.
Is CIRCIA reporting mandatory already?
No. The mandatory CIRCIA regulatory regime is still dependent on the final rule taking effect.
Can the same incident require both SEC and UK GDPR reporting?
Yes.
For example, a material ransomware incident involving UK personal data could potentially trigger both regimes.
Each requires a separate legal analysis because the triggers differ.
Final Takeaway
There is no single U.S. cyber-reporting deadline and no single UK cyber-reporting deadline.
The key 2026 comparison is:
SEC:
materiality determination → 4 business days
UK GDPR:
awareness of reportable personal data breach → 72 hours
CIRCIA proposed:
covered cyber incident → 72 hours
ransom payment → 24 hours
UK Cyber Security and Resilience Bill proposed:
qualifying incident awareness → 24-hour initial + 72-hour fuller report
The important operational principle is therefore:
one incident → many possible clocks
The strongest organizations maintain:
- one authoritative incident chronology;
- separate legal trigger analyses;
- predefined reporting owners;
- rapid supplier notification;
- clear executive escalation.
Cybersecurity teams should not ask only:
“When did we detect the attack?”
They should also ask:
“Which regulatory trigger has occurred, which clock is now running, and who owns the next filing?”
That is the real meaning of cyber incident reporting readiness in 2026.
Primary External Sources
Use these authoritative external links at the bottom of the WordPress article.
SEC — Cybersecurity Risk Management, Strategy, Governance and Incident Disclosure
The SEC confirms the Item 1.05 materiality trigger and four-business-day deadline.
SEC — Disclosure of Material and Other Cybersecurity Incidents
This explains Item 1.05 versus Item 8.01 and later amendments.
ICO — Personal Data Breaches: A Guide
This is the main UK GDPR breach-reporting guidance.
ICO — UK GDPR Data Breach Reporting
The ICO emphasizes risk assessment, 72-hour reporting and “report early, update later.”
GOV.UK — Cyber Security and Resilience Bill Incident Reporting
This confirms the proposed UK 24-hour initial and 72-hour fuller reporting structure.