SEC Cyber Incident Disclosure in 2026: Materiality, Form 8-K and Compliance Checklist
Cybersecurity incidents can quickly become securities-law issues for U.S. public companies.
When an attack occurs, technical teams naturally focus on containment, investigation and recovery. But public-company leadership must also answer another question:
Has the cybersecurity incident become material to investors?
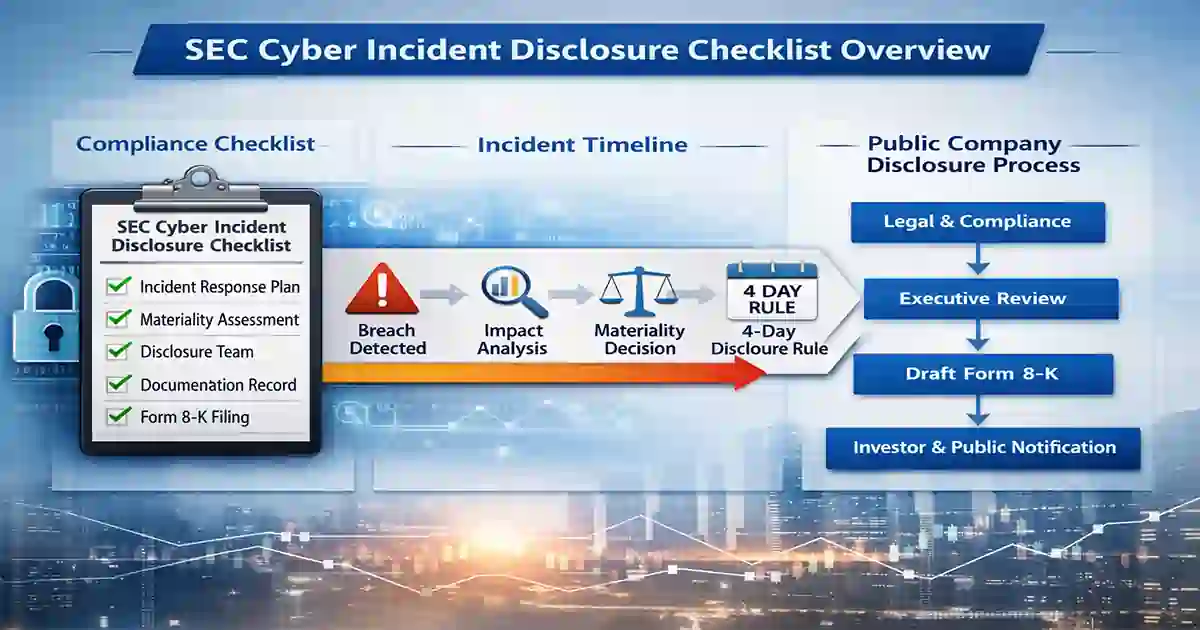
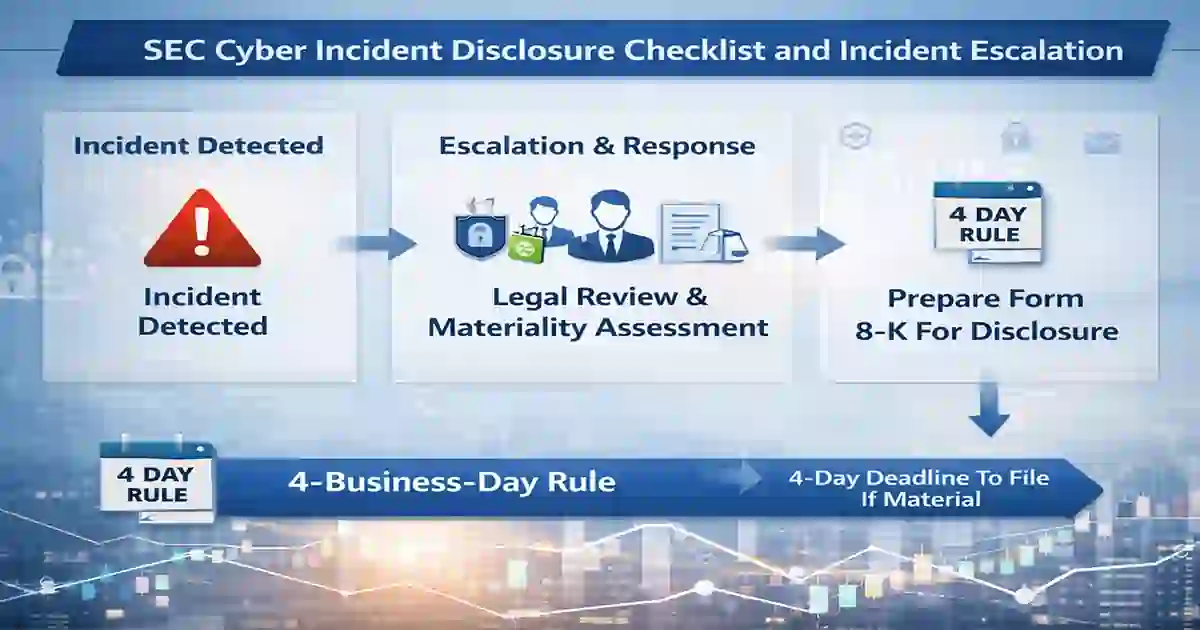
Under the SEC’s cybersecurity disclosure rules, a domestic registrant must disclose a material cybersecurity incident on Form 8-K under Item 1.05 generally within four business days after determining that the incident is material.
That distinction is critical.
The SEC filing clock is generally not triggered by the date of attack, the first alert, or even the date the incident is discovered.
It begins when the registrant determines—without unreasonable delay—that the cybersecurity incident is material.
For that reason, SEC cyber disclosure is not merely a filing exercise.
It requires a coordinated process involving:
- cybersecurity;
- legal;
- finance;
- investor relations;
- executive leadership;
- board oversight;
- communications;
- outside advisers where appropriate.
The central question for companies is:
Can we move from technical investigation to a defensible materiality decision quickly enough to meet the four-business-day filing deadline?
SEC Cyber Disclosure at a Glance
| Requirement | SEC rule |
|---|---|
| Incident covered | Material cybersecurity incident |
| Domestic registrant filing | Form 8-K, Item 1.05 |
| Main filing deadline | 4 business days after materiality determination |
| Materiality decision | Must be made without unreasonable delay |
| Main disclosure content | Material aspects of nature, scope, timing, and material impact or reasonably likely material impact |
| Technical details that could impede response | Not required |
| Voluntary non-material disclosure | May use Item 8.01 |
| Foreign private issuers | Form 6-K where applicable |
| Annual cyber governance disclosure | Regulation S-K Item 106 / Form 10-K |
| National-security/public-safety delay | Available through Attorney General determination |
The SEC’s compliance guide confirms these core requirements.
Table of Contents
What the Four-Business-Day Rule Actually Means
The most common misunderstanding is:
“We discovered the attack on Monday, so the Form 8-K is automatically due four business days later.”
That is not the SEC rule.
The Item 1.05 filing obligation is tied to the registrant’s materiality determination.
The SEC says the filing must generally be made within four business days after the company determines that the cybersecurity incident is material, and that the company must make that determination without unreasonable delay.
This creates two separate timelines:
Incident-response timeline
- attack occurs;
- monitoring detects activity;
- security confirms compromise;
- investigation expands.
Securities-disclosure timeline
- business impact becomes clearer;
- legal/finance/security evaluate significance;
- materiality determination is made;
- four-business-day filing clock begins.
The two timelines interact, but they are not the same.
Materiality Is the Core Decision
The SEC applies the traditional securities-law materiality standard.
Information is material if there is a substantial likelihood that a reasonable shareholder would consider it important when making an investment decision, or if the information would significantly alter the “total mix” of information available.
Cyber materiality therefore cannot be reduced to:
“Did we lose $10 million?”
A cyber incident may become material because of a combination of quantitative and qualitative effects.
Potential considerations include:
- operational disruption;
- revenue impact;
- business interruption;
- customer loss;
- regulatory exposure;
- litigation risk;
- intellectual property compromise;
- reputation;
- critical service disruption;
- strategic information theft;
- remediation cost;
- effects on financial reporting systems.
The SEC’s rule emphasizes material impact or reasonably likely material impact, including financial condition and results of operations.
Cybersecurity Time SEC Materiality Decision Matrix
A practical materiality review can use questions like these:
| Question | Example | Response |
|---|---|---|
| Is a critical business operation disrupted? | Production system unavailable | Escalate |
| Is revenue materially affected or at risk? | Sales platform offline | Quantify |
| Was sensitive or strategic information taken? | Source code or M&A data | Assess qualitative impact |
| Are customer relationships materially affected? | Large customer outage | Escalate |
| Could regulatory consequences be significant? | Multiple regulators involved | Legal review |
| Could litigation exposure be significant? | Sensitive data compromised | Assess |
| Could reputation affect business materially? | Major public trust issue | Consider |
| Would a reasonable investor view this as important? | Significant ongoing attack | Materiality review |
| Materiality determined? | Yes | Start 4-business-day clock |
This is an operational framework, not an official SEC scoring model.ll need to be made.
Detection Is Not Materiality
One of the most important documentation practices is to preserve different timestamps.
Detection time
When did security first identify suspicious activity?
Incident confirmation time
When did the organization determine that a genuine cybersecurity incident had occurred?
Materiality-review start time
When did the disclosure team begin evaluating securities-law implications?
Materiality-determination time
When did the company decide the incident was material?
The SEC clock is generally tied to the last of these.
Your current article correctly recognizes this distinction, but the rewritten version should make it much more explicit.
Do Not Delay Materiality Unreasonably
The fact that the clock begins at materiality determination does not permit a company to delay that determination intentionally.
The SEC specifically states that the materiality determination must be made without unreasonable delay.
That means companies should avoid practices such as:
- waiting for perfect forensic certainty;
- postponing legal escalation;
- avoiding executive review until containment is complete;
- delaying business-impact analysis merely to postpone disclosure.
The correct approach is:
investigate promptly + evaluate impact promptly + document uncertainty honestly.
Item 1.05 Form 8-K: What Must Be Disclosed?
For a material cybersecurity incident, Item 1.05 requires disclosure of:
- the material aspects of the nature of the incident;
- its scope;
- its timing;
- the material impact or reasonably likely material impact on the registrant.
This is investor-facing disclosure.
It is not intended to function as:
- a forensic report;
- an IOC list;
- a technical containment playbook;
- an architectural diagram.
The SEC explicitly says companies are not required to disclose technical information about their response, systems, networks, devices or vulnerabilities in such detail that disclosure would impede remediation or response.
What a Good Item 1.05 Disclosure Should Explain
A useful disclosure should answer investor-relevant questions such as:
- What happened?
- What part of the business was affected?
- When did the incident occur or become known?
- What impact has occurred?
- What impact is reasonably likely?
- Is the company still investigating?
- Are operations affected?
- Are financial consequences expected?
The language should be:
- factual;
- concise;
- understandable;
- consistent with known information.
Avoid:
- speculation;
- unnecessary technical jargon;
- unsupported reassurance;
- vague boilerplate.
What if Some Information Is Still Unknown?
An ongoing investigation does not automatically prevent filing.
The SEC’s instructions allow a registrant to state that required information has not yet been determined or is unavailable at the time of filing.
When the information later becomes available, the company must amend the Item 1.05 disclosure within the prescribed timeframe.
That supports an important operational rule:
A disclosure process should distinguish known facts, reasonable estimates and unknown facts.
Do not wait for complete certainty where the materiality determination has already been made.
Item 1.05 vs Item 8.01: A Critical Distinction
This deserves a dedicated section because many public companies initially misunderstood it.
The SEC clarified in May 2024 that Item 1.05 should be reserved for cybersecurity incidents that the company has determined are material.
If a company wants to voluntarily disclose:
- an incident that it has determined is immaterial; or
- an incident for which a materiality determination has not yet been made,
the SEC indicated that Item 8.01 can be used instead.
The SEC’s concern is investor confusion.
If non-material events are filed under Item 1.05, investors may reasonably assume the company has determined the incident to be material.
Practical rule
Material incident → Item 1.05
Voluntary non-material or not-yet-determined incident → consider Item 8.01
A voluntary Item 8.01 disclosure does not remove the requirement to continue evaluating materiality. If the company later determines the incident is material, Item 1.05 may still be required.
SEC Cyber Disclosure Workflow
A practical workflow looks like this:
1. Detect
Security identifies suspicious or malicious activity.
2. Investigate
Confirm:
- systems affected;
- attacker activity;
- operational impact;
- data exposure.
3. Escalate
Bring in:
- legal;
- finance;
- executive sponsor;
- investor relations.
4. Assess materiality
Apply quantitative and qualitative factors.
5. Document the decision
Record:
- facts considered;
- participants;
- uncertainties;
- exact time.
6. If material, start the filing clock
Prepare Form 8-K Item 1.05.
7. Coordinate communications
Ensure consistency across:
- SEC filing;
- customer communications;
- regulator notices;
- employee communications;
- public statements.
8. Continue investigation
Amend disclosures where required as material information becomes available.
First 24 Hours of a Potentially Material Cyber Incident
The SEC does not impose a universal 24-hour filing deadline, but the first 24 hours often determine whether the organization can make a timely materiality decision.
Hours 0–2
- activate incident response;
- preserve evidence;
- identify incident commander;
- record detection time.
Hours 2–6
Establish:
- affected systems;
- operational disruption;
- data exposure;
- customer impact;
- likely attack type.
Hours 6–12
Notify:
- General Counsel;
- CISO;
- CFO;
- appropriate executive sponsor.
Begin materiality analysis.
Hours 12–24
Document:
- known facts;
- unknown facts;
- estimated impacts;
- regulatory exposure;
- potential investor significance.
The goal is not necessarily to determine materiality within 24 hours.
The goal is to ensure the determination is not delayed because disclosure governance started too late.
For broader response sequencing, see the Cybersecurity Incident Response Timeline.
SEC Disclosure Team: Who Should Be Involved?
A potentially material cyber incident should not remain confined to the SOC.
A practical disclosure team may include:
- General Counsel;
- CISO;
- CFO;
- CEO or delegated executive;
- investor relations;
- communications;
- privacy/compliance;
- controller or accounting leadership;
- outside counsel;
- external forensic advisers where appropriate.
The exact composition varies by company.
What matters is that the team is named before an incident.
Cybersecurity Time SEC Disclosure RACI
| Activity | Primary owner | Supporting teams |
|---|---|---|
| Detection | SOC | IT/Cloud |
| Technical investigation | Incident Response | Forensics |
| Business-impact assessment | Business/Finance | Security |
| Materiality assessment | Legal + Executive | Finance, Security |
| Materiality decision record | Legal/Corporate Secretary | Executive team |
| Form 8-K drafting | Legal/SEC Reporting | IR, Finance |
| Filing approval | Authorized executive | Legal |
| External communication | IR/Communications | Legal |
| Amendment evaluation | Legal | IR, Security |
| Board update | Executive/Corporate Secretary | CISO |
This is an example governance structure, not an SEC-mandated RACI.
National-Security or Public-Safety Disclosure Delay
The SEC rules permit a delay in Item 1.05 disclosure in a narrow circumstance.
Disclosure may be delayed if the United States Attorney General determines that immediate disclosure would pose a substantial risk to national security or public safety and notifies the SEC in writing.
This is not a company-controlled delay.
A registrant cannot simply decide internally:
“Disclosure may harm national security, so we will wait.”
The formal process requires government involvement.
This issue should therefore be incorporated into incident-response planning for companies operating in:
- defense;
- critical infrastructure;
- national-security-sensitive industries.
Foreign Private Issuers
The SEC’s cybersecurity disclosure rules also affect foreign private issuers.
The SEC’s compliance guide explains that FPIs generally use Form 6-K for material cybersecurity incidents when the information is:
- disclosed or required to be disclosed in a foreign jurisdiction;
- disclosed or required by a foreign stock exchange; or
- distributed to security holders.
FPIs also have annual cybersecurity disclosure requirements through Form 20-F.
This makes multinational reporting coordination particularly important.
Annual Cybersecurity Disclosure: Regulation S-K Item 106
The SEC cyber rules are not limited to incident reporting.
Regulation S-K Item 106 requires annual disclosures regarding:
- processes for assessing, identifying and managing material cybersecurity risks;
- whether cyber risks or prior incidents have materially affected or are reasonably likely to materially affect the company;
- board oversight of cybersecurity risk;
- management’s role in assessing and managing cybersecurity risk.
Domestic registrants include this information in Form 10-K.
Foreign private issuers provide comparable disclosure in Form 20-F.
That means SEC cybersecurity compliance involves two related programs:
incident disclosure
and
annual risk/governance disclosure.
Board Oversight Matters
Cybersecurity governance is now investor-facing.
Companies should be able to explain:
- which board committee oversees cyber risk;
- how frequently management briefs the board;
- how material risks are escalated;
- management roles responsible for cybersecurity;
- how cyber risk integrates into enterprise risk management.
For practical governance metrics, see the Board-Level Cybersecurity Metrics Guide.
Third-Party Incidents Can Still Become Material
A cybersecurity incident does not have to originate inside the registrant’s own network to create disclosure risk.
A material event may involve:
- cloud provider;
- payment processor;
- MSP;
- SaaS platform;
- software supplier;
- customer-facing technology partner.
The investor-facing question remains:
What is the material impact on the registrant?
That makes supplier notification speed important.
If a vendor waits five days to inform the company, the company may lose valuable time for:
- investigation;
- materiality assessment;
- regulatory analysis.
Use the Third-Party Risk Assessment Checklist to improve supplier governance.
SEC vs CIRCIA
Public critical-infrastructure companies may eventually need to manage both systems.
| Topic | SEC | CIRCIA proposed framework |
|---|---|---|
| Primary audience | Investors / SEC | CISA / government |
| Who may be covered | SEC registrants | Covered critical-infrastructure entities |
| Trigger | Materiality determination | Covered cyber incident |
| Main deadline | 4 business days | Proposed 72 hours |
| Ransom payment | No separate 24h SEC payment report | Proposed 24 hours |
| Materiality required? | Yes | Different covered-incident standard |
| Public filing? | Yes | Government reporting |
CIRCIA’s mandatory reporting regime was still not effective at the time of this September 2026 review, while the SEC’s Item 1.05 framework is already operational.
For the current CIRCIA status, see CIRCIA 2026 Reporting Readiness.
SEC vs State Breach Notification
The SEC rule also does not replace state data-breach notification laws.
A single cybersecurity incident might create:
- SEC disclosure;
- state attorney-general notification;
- consumer notification;
- sector regulator notification;
- contractual notice.
Those triggers can be very different.
For example:
SEC: investor materiality.
State privacy law: particular categories of personal information and affected residents.
A company should maintain one incident record capable of supporting multiple reporting paths.
Build a Materiality Evidence Package
Companies should preserve the evidence supporting both the decision and its timing.
Include:
Technical facts
- affected systems;
- attacker activity;
- persistence;
- data accessed;
- remediation status.
Business impact
- service outage;
- production impact;
- revenue effects;
- customer consequences.
Financial assessment
- response costs;
- lost revenue;
- insurance;
- remediation expenses.
Legal and regulatory impact
- privacy laws;
- lawsuits;
- regulator involvement.
Governance record
- disclosure-team meetings;
- materiality discussions;
- decision timestamp;
- board briefings.
This record can become extremely important if the company’s disclosure timing is later questioned.
Common SEC Cyber Disclosure Errors
1. Treating Cybersecurity as an IT-Only Issue
Materiality is a business and investor question.
Security alone cannot determine it.
2. Waiting for Complete Forensic Certainty
The company should gather enough information for a reasonable decision, not wait indefinitely for every technical detail.
3. Delaying Materiality Review
The SEC requires the determination to be made without unreasonable delay.
4. Using Item 1.05 for Every Cyber Event
The SEC has specifically warned against using Item 1.05 for voluntary disclosure of non-material or not-yet-determined incidents because it may confuse investors.
Use Item 8.01 where appropriate for voluntary disclosure.
5. Failing to Record the Materiality Timestamp
If no one can identify precisely when materiality was determined, calculating the filing deadline becomes much harder.
6. Overloading the Filing With Technical Detail
Do not publish information that could impede response or remediation.
The SEC does not require that level of technical detail.
7. Using Boilerplate Language
Disclosure should explain what is materially important about the actual incident.
Generic language may not give investors decision-useful information.
8. Ignoring Supplier Incidents
Third-party incidents may still materially affect the registrant.
9. Forgetting Annual Item 106 Disclosures
Cyber compliance is not limited to Item 1.05.
Risk management, governance and board oversight are annual disclosure subjects too.
SEC Cyber Incident Disclosure Checklist
Use this before and during a potentially material incident.
Incident response
- Incident ID created
- Detection time recorded
- Incident confirmed
- Evidence preserved
- Business impact assessed
Disclosure governance
- General Counsel engaged
- CISO engaged
- CFO engaged
- Investor relations informed
- Executive sponsor identified
Materiality
- Quantitative impact evaluated
- Qualitative impact evaluated
- Reasonable-investor perspective considered
- Materiality decision documented
- Decision timestamp recorded
Filing
- Item 1.05 vs Item 8.01 determined
- Four-business-day deadline calculated
- Draft reviewed
- Unknown facts clearly identified
- Filing approved
Communications
- Customer messaging aligned
- Board messaging aligned
- Regulator messaging aligned
- Media/IR messaging aligned
Follow-up
- Ongoing investigation monitored
- Amendment need assessed
- Annual Item 106 implications reviewed
- Lessons learned captured
Run an SEC Disclosure Tabletop
A good exercise can reveal gaps before a real filing deadline.
Scenario
Monday 08:00:
SOC detects suspicious administrator access.
Monday 14:00:
Forensics confirms data exfiltration.
Tuesday morning:
A major customer-facing system is disrupted.
Tuesday afternoon:
Finance estimates possible material revenue impact.
Ask:
- When was the incident detected?
- When was it confirmed?
- When did materiality review begin?
- What information is still unknown?
- Who has authority to make the materiality determination?
- If materiality is determined Tuesday at 16:00, when is the filing deadline?
- What goes into Item 1.05?
- Is an Item 8.01 voluntary filing being considered before materiality?
- Are other regulators involved?
- Who informs the board?
The purpose is to test the decision process, not merely the ability to draft a form.
Frequently Asked Questions
Does every cyber incident require a Form 8-K?
No.
Item 1.05 applies when the registrant determines that a cybersecurity incident is material.
When does the four-business-day clock start?
Generally when the company determines that the cybersecurity incident is material, not when the attack was first detected.
Can a company delay making the materiality determination?
The determination must be made without unreasonable delay.
What must Item 1.05 disclose?
Material aspects of:
- nature;
- scope;
- timing;
and the incident’s material impact or reasonably likely material impact.
Must the company disclose technical vulnerabilities?
Not in detail if doing so would impede response or remediation.
Can a non-material incident be disclosed voluntarily?
Yes.
The SEC has indicated companies may voluntarily disclose an incident under Item 8.01, including where materiality has not yet been determined or the event is considered immaterial.
Does an Item 8.01 filing end the materiality review?
No.
The company must continue evaluating the incident. If it later determines the incident is material, Item 1.05 may still be required.
Can disclosure be delayed for national-security reasons?
Yes, but only through the formal process where the U.S. Attorney General determines immediate disclosure would pose a substantial risk to national security or public safety and provides written notice to the SEC.
What do foreign private issuers use?
FPIs generally use Form 6-K for current-reporting obligations under the rule and Form 20-F for annual cybersecurity disclosures.
What is Item 106?
Regulation S-K Item 106 requires annual disclosure of cybersecurity:
- risk-management processes;
- strategy;
- management’s role;
- board oversight.
Final Takeaway
The SEC cybersecurity disclosure rule is not primarily a four-day drafting exercise.
The real challenge happens before the clock starts.
Companies need to move efficiently through:
detect → investigate → assess business impact → evaluate materiality → document the decision → disclose
The core rule is:
material cybersecurity incident → Form 8-K Item 1.05 → generally within four business days after materiality determination.
But strong compliance also requires:
- timely materiality review;
- clear decision ownership;
- careful documentation;
- Item 1.05 vs Item 8.01 discipline;
- coordination with suppliers;
- consistent public communications;
- annual Item 106 governance disclosure.
The strongest disclosure process is one in which legal, cybersecurity, finance and leadership already know their roles before the incident begins.
Four business days is enough time to file when the organization does not spend the first three days deciding who owns the decision.
Primary External Sources
Use a compact authoritative source section.
SEC — Cybersecurity Risk Management, Strategy, Governance and Incident Disclosure
This is the SEC’s primary rule page.
SEC — Small Entity Compliance Guide
This clearly explains Item 1.05, the four-business-day deadline, foreign private issuers and Item 106.
SEC — Disclosure of Material and Other Cybersecurity Incidents
This SEC statement clarifies Item 1.05 versus voluntary Item 8.01 disclosure.
SEC — Cybersecurity Rule Adoption Release
This provides the core disclosure requirements and national-security delay framework.
NIST SP 800-61 Rev. 3 — Incident Response
Use NIST as supporting operational guidance, not as the source for SEC legal requirements.