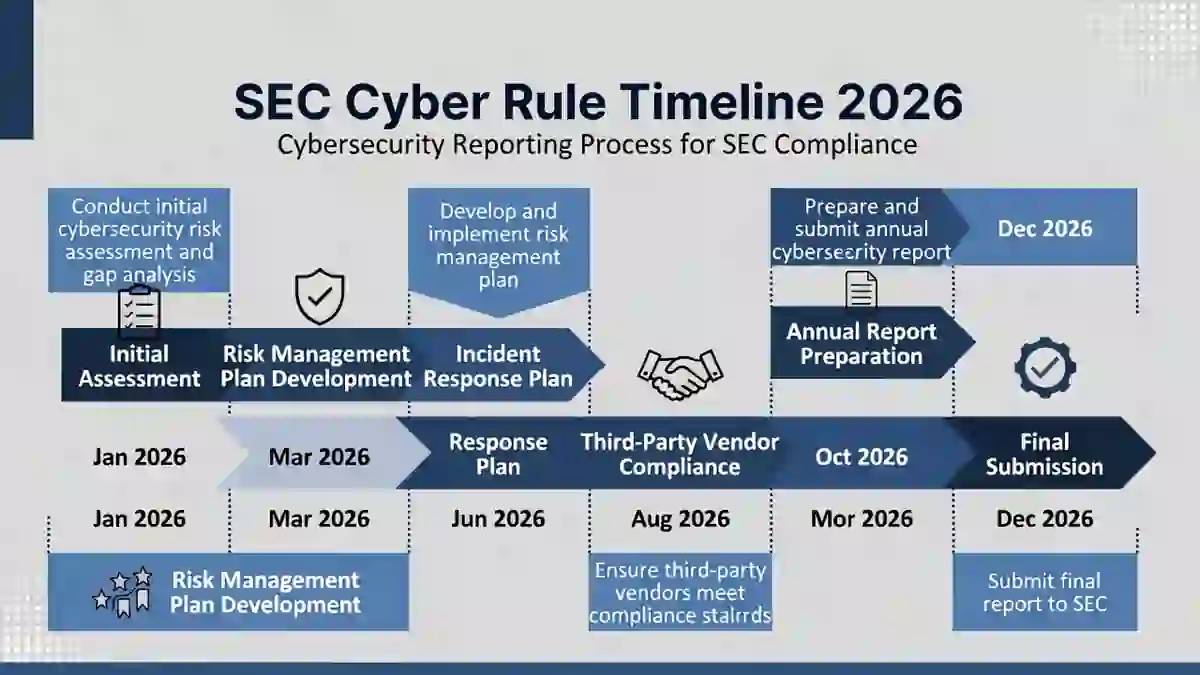
SEC Cybersecurity Rule Timeline 2026: Form 8-K, Materiality and Annual Disclosure Deadlines
The SEC cybersecurity rules created a permanent disclosure framework for U.S. public companies.
By 2026, the most important issue is not learning a new set of calendar deadlines. It is understanding which event starts each disclosure obligation.
For a domestic SEC registrant, a cybersecurity incident does not automatically trigger a Form 8-K merely because it was detected.
Instead, the key sequence is:
cyber incident → investigation → materiality determination → Form 8-K Item 1.05
The SEC requires an Item 1.05 Form 8-K generally within four business days after the registrant determines that the cybersecurity incident is material. The materiality determination itself must be made without unreasonable delay.
That distinction is essential because companies often confuse:
- the date the attack started;
- the date the incident was discovered;
- the date the incident was confirmed;
- the date materiality was determined;
- the filing deadline.
They are not necessarily the same.
SEC Cyber Rule Timeline at a Glance
| Event | SEC consequence |
|---|---|
| Cyber incident occurs | No automatic Form 8-K deadline |
| Incident detected | Begin investigation |
| Incident confirmed | Begin/continue impact assessment |
| Materiality review | Evaluate quantitative and qualitative effects |
| Materiality determined | 4-business-day Item 1.05 clock begins |
| Some required information unavailable | File known facts and amend later as required |
| Voluntary disclosure before materiality determination | Consider Item 8.01 |
| Annual reporting cycle | Item 106 disclosures in Form 10-K |
| Foreign private issuer event | Form 6-K rules may apply |
| National-security/public-safety concern | Formal Attorney General delay process may apply |
This is the timeline companies should operationalize.
Table of Contents
What the SEC Cybersecurity Rules Cover
The SEC’s cybersecurity framework has two main components.
1. Material Cybersecurity Incident Disclosure
Domestic registrants use Form 8-K Item 1.05 to disclose material cybersecurity incidents.
The required disclosure covers:
- material aspects of the incident’s nature;
- scope;
- timing;
- material impact or reasonably likely material impact.
2. Annual Cybersecurity Risk and Governance Disclosure
Regulation S-K Item 106 requires companies to describe:
- processes for assessing, identifying and managing material cybersecurity risks;
- whether cybersecurity risks or previous incidents have materially affected or are reasonably likely to materially affect the company;
- board oversight;
- management’s role.
Domestic registrants provide this information in Form 10-K, while foreign private issuers provide comparable disclosures under Form 20-F.
That means SEC cybersecurity compliance has two timelines:
event-driven disclosure
and
annual governance disclosure.
The Four-Business-Day Rule Explained
The most important timing rule is:
A domestic registrant generally must file Form 8-K Item 1.05 within four business days after determining that a cybersecurity incident is material.
The SEC does not say:
Four days after the attack occurs.
It does not say:
Four days after detection.
And it does not say:
Four days after the security team confirms compromise.
The clock is linked to the materiality determination.
Materiality Cannot Be Delayed Unreasonably
This does not allow a company to postpone the decision indefinitely.
The SEC requires the materiality determination to be made without unreasonable delay.
A weak process might look like:
Monday: Security confirms major compromise
Tuesday: Legal not involved
Wednesday: Finance starts impact analysis
Thursday: Executive team first hears about incident
Friday: Materiality review finally starts
That creates unnecessary regulatory risk.
A better process is:
detection → technical validation → business impact assessment → legal review → materiality decision
with those activities happening in parallel where possible.
SEC Materiality Standard
Cybersecurity does not have a special numerical materiality threshold.
The SEC applies the long-standing securities-law standard.
Information is material when there is a substantial likelihood that a reasonable shareholder would consider it important in making an investment decision, or when it would significantly alter the total mix of available information.
That means a cyber incident may be material even when immediate financial loss is not enormous.
Relevant factors may include:
- revenue loss;
- business interruption;
- inability to provide critical services;
- customer loss;
- regulatory exposure;
- litigation;
- intellectual property theft;
- reputational consequences;
- impact on financial reporting;
- strategic data compromise.
The assessment should consider both quantitative and qualitative factors.
Cybersecurity Time SEC Materiality Timeline
| Stage | Example | SEC relevance |
|---|---|---|
| Attack begins | Threat actor gains access | No automatic filing clock |
| Detection | SOC alert fires | Investigation begins |
| Confirmation | Unauthorized access verified | Impact analysis accelerates |
| Business assessment | Revenue/customer impact identified | Materiality review |
| Materiality determination | Executive/legal decision | 4-business-day clock starts |
| Item 1.05 filing | Form 8-K filed | Mandatory disclosure complete |
| New required facts later available | Scope becomes clearer | Amendment may be required |
This is a practical operational framework, not an official SEC table.
What Must Be Disclosed Under Item 1.05?
Item 1.05 requires disclosure of the material aspects of:
- nature;
- scope;
- timing;
and the incident’s:
- material impact; or
- reasonably likely material impact.
The SEC does not require detailed information about:
- exact vulnerabilities;
- response architecture;
- security controls;
- network design;
- planned remediation;
where that level of detail could impede response or remediation.
This is an investor disclosure, not a forensic report.
What If the Company Does Not Yet Know Everything?
A material incident may still be under investigation when the four-business-day deadline arrives.
The SEC allows a company to state that required information is not yet determined or unavailable.
When that information becomes available, the company must file an amendment within the applicable timeframe. The SEC’s 2024 clarification explains that the amendment is generally due within four business days after the information is determined or becomes available, without unreasonable delay.
That creates a useful discipline:
known → disclose
unknown → identify as unknown
later determined → amend
Do not wait for complete forensic closure if materiality has already been determined.
Item 1.05 vs Item 8.01
This is one of the most important SEC cyber disclosure distinctions.
The SEC clarified in May 2024 that Item 1.05 is for cybersecurity incidents the company has determined are material.
If a company voluntarily chooses to disclose:
- an incident determined to be immaterial; or
- an incident where materiality has not yet been determined,
the SEC encourages use of another Form 8-K item, such as Item 8.01.
The reason is investor clarity.
If companies use Item 1.05 for every incident, investors may incorrectly infer that all those events were material.
Voluntary Disclosure Does Not Stop the Materiality Review
Suppose a company files an Item 8.01 voluntarily on Monday.
On Wednesday, additional facts show the incident is material.
The company still has to make the materiality determination and then file an Item 1.05 Form 8-K within four business days of that determination.
The earlier voluntary filing does not replace the mandatory Item 1.05 obligation.
Worked SEC Timeline Example
Consider this hypothetical incident.
Monday, 08:00
SOC detects unusual authentication activity.
No SEC filing deadline has started.
Monday, 15:00
Incident-response team confirms unauthorized access.
Still no automatic four-day Item 1.05 clock.
Tuesday, 10:00
Investigation shows customer-facing systems are affected.
Materiality review intensifies.
Tuesday, 16:00
Management and legal determine that the incident is material.
This is the key SEC timestamp.
The four-business-day Form 8-K period now begins.
The company should calculate the filing deadline based on business days and applicable SEC filing rules.
The important lesson is:
detection Monday ≠ automatic Monday SEC clock
materiality determination Tuesday = SEC filing clock trigger
Detection Speed Still Matters
Although detection does not itself trigger the SEC’s four-business-day deadline, detection quality still matters greatly.
Slow detection can increase:
- attacker dwell time;
- operational damage;
- data loss;
- financial consequences;
- customer impact;
- likelihood that the event becomes material.
NIST’s current incident-response guidance, SP 800-61 Rev. 3, emphasizes integrating preparation, detection, response and recovery into enterprise cybersecurity risk management.
For practical detection metrics, see Cybersecurity Time’s Mean Time to Detect.
Four Different Timestamps to Record
Public companies should preserve at least four separate timestamps.
1. Detection
When did monitoring first identify suspicious activity?
2. Incident Confirmation
When did responders determine the event was a genuine cybersecurity incident?
3. Materiality Review Start
When did the company begin formal securities-law analysis?
4. Materiality Determination
When did the registrant determine the event was material?
The last timestamp normally drives the Item 1.05 deadline.
Cybersecurity Time SEC Disclosure Clock Record
For every potentially material event, maintain:
| Field | Example |
|---|---|
| Detection | 9 Sept 2026, 07:45 |
| Incident confirmed | 9 Sept, 11:30 |
| Legal escalated | 9 Sept, 12:10 |
| Materiality review initiated | 9 Sept, 14:00 |
| Materiality determined | 10 Sept, 09:15 |
| Item 1.05 due | Calculated from materiality decision |
| Item 1.05 filed | Actual EDGAR timestamp |
| Amendment needed? | Yes/No |
This becomes useful governance evidence if disclosure timing is later questioned.
National-Security and Public-Safety Delay
The SEC rules provide a narrow formal delay mechanism.
An Item 1.05 filing may be delayed if the U.S. Attorney General determines that immediate disclosure would pose a substantial risk to national security or public safety and provides written notification to the SEC.
This is not a normal company-controlled extension.
A company cannot simply decide internally:
“This looks sensitive, so we will delay disclosure.”
Organizations operating in defense or critical infrastructure should understand the formal Department of Justice process before an incident occurs.
Foreign Private Issuer Timeline
Foreign private issuers operate under a related but different reporting mechanism.
The SEC says a foreign private issuer must furnish material cybersecurity incident information on Form 6-K promptly after the information is:
- disclosed or required to be disclosed in a foreign jurisdiction;
- disclosed or required by a foreign stock exchange; or
- distributed to security holders.
For annual cybersecurity risk, strategy and governance disclosure, FPIs use Form 20-F.
This means multinational companies need to coordinate U.S. disclosure with home-country and exchange requirements.
Annual Item 106 Timeline
SEC cybersecurity compliance does not end after an incident filing.
Regulation S-K Item 106 requires annual disclosures covering cybersecurity:
- risk management;
- strategy;
- board oversight;
- management’s role.
Domestic companies include this information in Form 10-K.
Unlike Item 1.05, this is not triggered by a specific cyber incident.
It follows the company’s normal annual-reporting cycle.
What Item 106 Requires Companies to Explain
Companies need to describe their processes, if any, for assessing, identifying and managing material risks from cybersecurity threats.
They must also describe whether cyber risks, including risks from previous incidents, have materially affected or are reasonably likely to materially affect:
- business strategy;
- results of operations;
- financial condition.
The governance section requires disclosure of:
- board oversight of cybersecurity risk;
- applicable board committee/subcommittee;
- management’s role in assessing and managing material cybersecurity risk.
Board Oversight Is Not a Separate Four-Day Deadline
Your existing article combines incident reporting and board governance as if both belong to one “SEC Cyber Rule Timeline.”
They are related, but different.
Item 1.05
Event-driven
Triggered by materiality determination.
Item 106
Annual
Reported through Form 10-K governance/risk disclosure.
Separating these improves both technical accuracy and reader understanding.
SEC Timeline vs CIRCIA
This comparison is particularly useful for critical-infrastructure public companies.
| Topic | SEC | CIRCIA proposed framework |
|---|---|---|
| Trigger | Materiality determination | Covered cyber incident |
| Deadline | 4 business days | Proposed 72 hours |
| Ransom-payment report | No separate 24h SEC rule | Proposed 24h |
| Primary audience | Investors / SEC | CISA |
| Public disclosure | Yes | Government reporting |
| Current status | Active | Final mandatory rule not yet effective as of Sept 2026 |
For a detailed CIRCIA readiness guide, see CIRCIA 2026.
One incident may ultimately require several different regulatory workflows.
SEC Timeline vs State Breach Laws
The SEC’s securities-law trigger is materiality to investors.
State breach-notification laws often focus on:
- affected residents;
- defined categories of personal information;
- risk of harm;
- state-specific timing.
Therefore:
material SEC incident ≠ automatically state-notifiable
and:
state-notifiable data breach ≠ automatically SEC-material
The same event needs separate legal analyses.
Do Customer and Partner Communications Have to Stop Until the 8-K Is Filed?
No.
SEC staff clarified in June 2024 that Item 1.05 does not prevent companies from sharing information about a material cybersecurity incident with:
- customers;
- commercial counterparties;
- other parties,
where appropriate.
Companies still need to consider other securities-law requirements, including selective disclosure concerns, but the cyber rule itself does not create a blanket prohibition on necessary operational communications.
This is an important point for:
- suppliers;
- customers;
- insurers;
- incident-response partners.
Recommended SEC Incident Timeline Workflow
Stage 1 — Detection
Owner:
SOC / IT security
Actions:
- identify event;
- preserve evidence;
- open incident.
Stage 2 — Technical Investigation
Owner:
Incident Response
Actions:
- identify scope;
- determine data/service impact;
- estimate attacker activity.
Stage 3 — Business Impact Analysis
Owners:
Security + Finance + Business + Legal
Actions:
- quantify disruption;
- assess customer effects;
- estimate financial consequences.
Stage 4 — Materiality Determination
Owners:
Legal + Executive Leadership
Actions:
- apply reasonable-investor standard;
- consider quantitative/qualitative factors;
- document decision/time.
Stage 5 — Disclosure
Owner:
SEC Reporting / Legal
Actions:
- calculate four-business-day deadline;
- draft Item 1.05;
- coordinate IR/communications;
- file.
Stage 6 — Updates
Actions:
- monitor investigation;
- determine whether amendment is required;
- maintain consistent communications.
SEC Cyber Timeline RACI
| Activity | Primary owner | Supporting teams |
|---|---|---|
| Detect incident | SOC | IT |
| Confirm incident | IR Lead | Forensics |
| Evaluate business impact | Business/Finance | Security |
| Assess materiality | Legal | Finance, Security |
| Determine materiality | Authorized management | Legal |
| Calculate filing deadline | SEC Reporting | Legal |
| Draft Item 1.05 | Legal/SEC Reporting | IR, Finance |
| Investor communications | Investor Relations | Legal |
| Board briefing | Executive/Corporate Secretary | CISO |
| Amendment assessment | Legal | IR, Security |
This is an example governance model, not an SEC-required organizational chart.
SEC Cybersecurity Timeline Checklist
Before an incident
- materiality process documented;
- SEC disclosure team named;
- outside counsel contacts available;
- escalation thresholds documented;
- board reporting process established.
During investigation
- detection time recorded;
- incident-confirmation time recorded;
- business impact assessed;
- legal engaged early;
- materiality review initiated.
At materiality determination
- decision documented;
- exact time recorded;
- four-business-day deadline calculated;
- Item 1.05 drafting begins.
Filing
- nature explained;
- scope explained;
- timing explained;
- material impact explained;
- unknown information identified;
- sensitive technical detail excluded.
After filing
- investigation continues;
- amendment need monitored;
- customers/partners updated where appropriate;
- board updated;
- annual Item 106 implications reviewed.
Common SEC Timeline Errors
Error 1: Starting the clock at detection
The four-business-day Item 1.05 clock is tied to materiality determination.
Error 2: Waiting too long to decide materiality
The determination must be made without unreasonable delay.
Error 3: Treating Item 1.05 as a voluntary cyber-update section
SEC staff encourages voluntary non-material or not-yet-determined cyber updates under Item 8.01 instead.
Error 4: Waiting for complete technical certainty
A material filing can state that certain required facts are not yet known and be amended later.
Error 5: Publishing too much technical detail
The SEC does not require response or vulnerability detail that would impede remediation.
Error 6: Confusing incident disclosure with annual governance disclosure
Item 1.05 and Item 106 serve different purposes and different timelines.
Error 7: Treating disclosure as solely a legal task
Materiality analysis requires input from:
- security;
- finance;
- operations;
- executive leadership.
Run an SEC Timeline Tabletop
Use a scenario that forces teams to distinguish detection from materiality.
Scenario
Monday 07:30
Suspicious activity detected.
Monday 16:00
Unauthorized access confirmed.
Tuesday 11:00
Investigation finds operational disruption.
Wednesday 09:00
Finance identifies a potentially significant revenue impact.
Wednesday 14:00
Company determines the incident is material.
Ask:
- When did the incident occur?
- When was it detected?
- When was it confirmed?
- When did the materiality review begin?
- When was materiality determined?
- When does the SEC filing clock start?
- What should be disclosed?
- What remains unknown?
- Does Item 8.01 have any role?
- Does another regulator also require reporting?
This exercise teaches teams to think in regulatory triggers, not simply dates.
Frequently Asked Questions
What starts the SEC four-business-day cyber disclosure clock?
The company’s determination that the cybersecurity incident is material.
Does the clock start when the attack is discovered?
Not automatically.
Discovery triggers investigation, but the Item 1.05 deadline generally begins when materiality is determined.
Can the company wait until the forensic investigation is complete?
The SEC requires the materiality decision to be made without unreasonable delay. Complete forensic certainty is not necessarily required.
What happens if some required information is unavailable?
The filing can state that information is not yet determined or unavailable, and the company may need to amend the filing when the information becomes available.
Should an immaterial incident be filed under Item 1.05?
SEC staff has encouraged companies to use another Form 8-K item, such as Item 8.01, for voluntary disclosure of immaterial or not-yet-determined incidents.
What is the annual SEC cybersecurity disclosure?
Regulation S-K Item 106 requires annual disclosures about cybersecurity risk-management processes, material cyber-risk effects, board oversight and management’s role.
What form do foreign private issuers use?
FPIs use Form 6-K for applicable current cyber disclosures and Form 20-F for annual cybersecurity risk and governance disclosure.
Can SEC disclosure be delayed for national-security reasons?
Yes, through the formal process where the U.S. Attorney General determines immediate disclosure would pose a substantial risk to national security or public safety and notifies the SEC.
Final Takeaway
The SEC cybersecurity rule does not create one universal “four-day cyber incident deadline.”
The real timeline is:
detect
↓
investigate
↓
evaluate impact
↓
determine materiality without unreasonable delay
↓
file Item 1.05 within four business days
That distinction is the most important lesson for executives, boards, legal teams and incident responders.
The SEC rules also create separate obligations for:
- voluntary disclosure under Item 8.01;
- later amendments;
- annual Item 106 governance/risk disclosures;
- foreign private issuers.
The strongest compliance programs therefore do not merely track filing dates.
They track decision points.
For public companies, the critical timestamp is not simply:
“When did the attack happen?”
It is:
“When did we determine that investors would consider this incident material?”
That is the timestamp around which the SEC disclosure process is built.
Primary External Sources
Use these authoritative sources at the bottom of the WordPress article:
SEC — Cybersecurity Risk Management, Strategy, Governance and Incident Disclosure
This is the clearest official guide to Item 1.05, Item 106, Form 6-K and Form 20-F.
SEC — Disclosure of Material and Other Cybersecurity Incidents
This clarifies Item 1.05 vs Item 8.01.
SEC — Cybersecurity Rule Adoption Release
This explains the four-business-day deadline and national-security/public-safety delay.
NIST finalized Revision 3 in April 2025 and says incident response should be integrated throughout cybersecurity risk management.